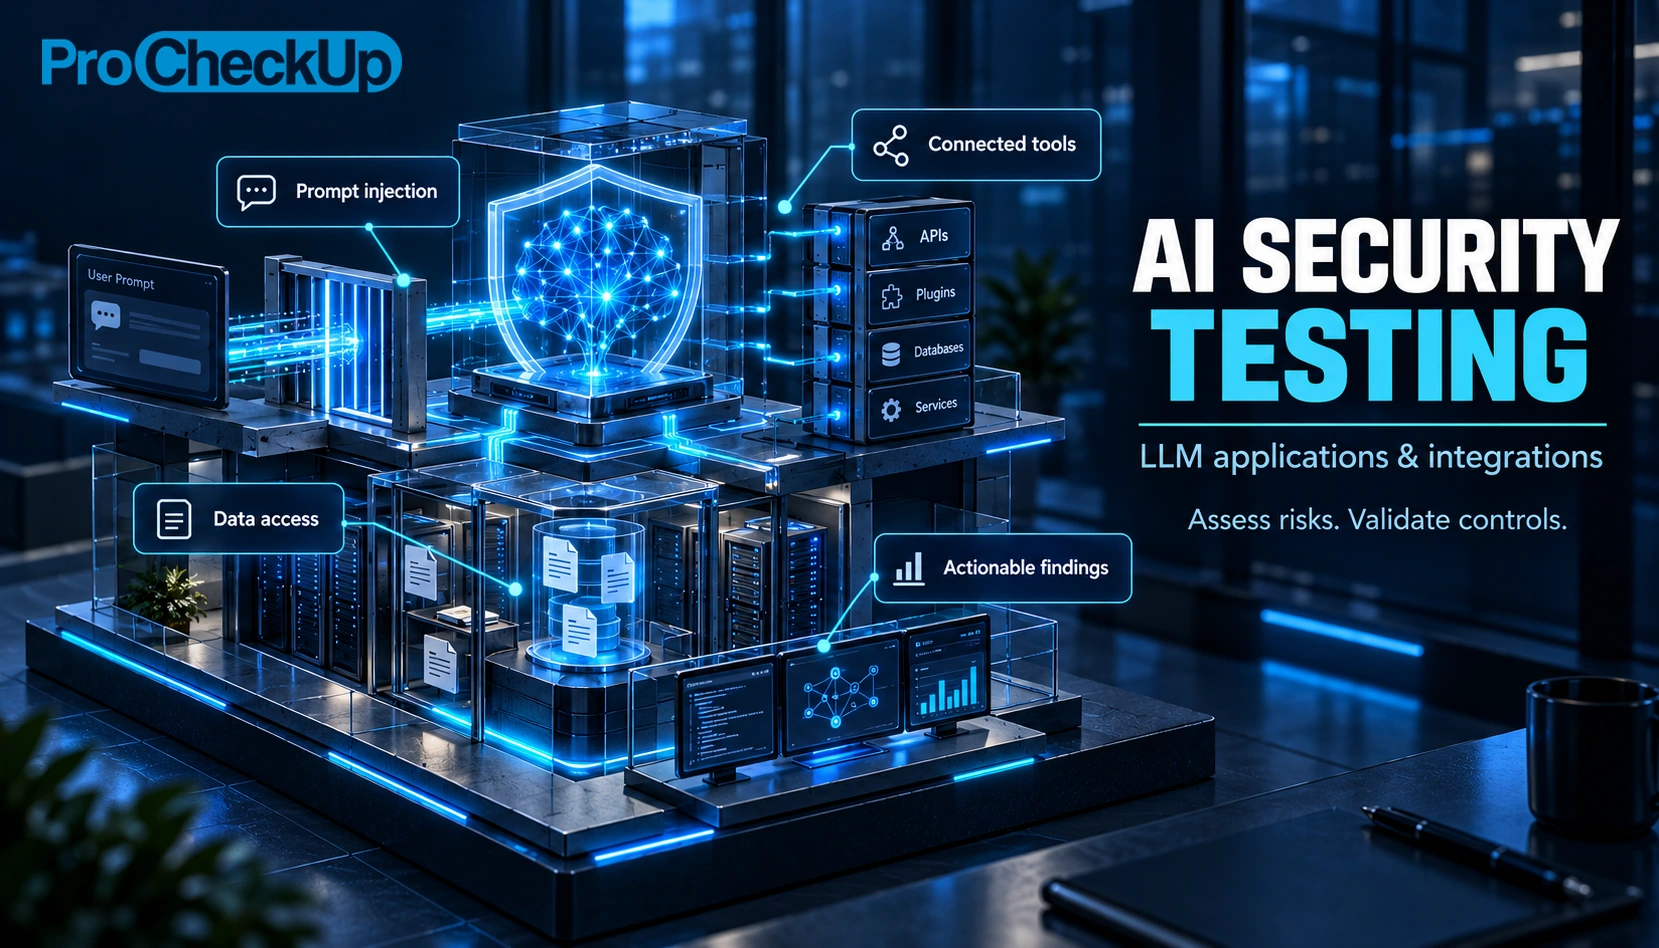
AI security testing examines whether an AI application can expose sensitive information, bypass access controls or be manipulated into unintended behaviour. ProCheckUp provides penetration testing for generative AI and large language model (LLM) applications, assessing the application and its integrations as well as the way it responds to prompts.
Whether you are preparing an internal assistant for deployment or adding AI features to a customer-facing service, an assessment helps your team understand exploitable weaknesses and prioritise practical improvements. The scope is agreed around your architecture, users, data and business objectives.
Discuss an AI security assessment or read about our generative AI testing experience.
AI security testing: contents
When to test an AI application
Consider an assessment before release, after a significant change to models or integrations, or when an existing application gains access to more sensitive information or additional actions. Common situations include:
Launching a customer-support chatbot or an internal knowledge assistant.
Connecting an LLM to documents, databases or a retrieval-augmented generation (RAG) system.
Adding AI functionality to an existing web application or API.
Giving an assistant access to business tools or workflows.
Responding to a customer assurance request or verifying security fixes.
What an AI security assessment can cover
The assessment follows the system's actual trust boundaries. During scoping, we identify the relevant scenarios, the access needed to test them and any restrictions on third-party services. Not every scenario applies to every application.
Prompt injection and instruction handling
Assess whether user prompts or content processed from documents and other sources can change the application's intended behaviour. The focus is the resulting security impact, such as exposing restricted information or influencing a connected action.
Sensitive information and access controls
Examine how the application separates users, roles and data. For systems using retrieval, agree tests of whether the information returned respects the user's permissions and the boundaries between different customers or teams.
Output handling and application security
Review how generated content is rendered, stored or passed to other systems. AI-specific testing should sit alongside assessment of the surrounding application's authentication, authorisation, input handling and APIs.
Connected tools and excessive permissions
Where an assistant can call APIs or perform actions, define the permitted tools, identities and approval steps. Agree scenarios that examine whether those controls restrict actions to the intended user and purpose. Tell us about agentic workflows and Model Context Protocol (MCP) integrations during scoping so their suitability for assessment can be established.
Resource use and operational limits
Consider controls intended to limit excessive requests, resource consumption and unexpected operating costs. Any availability or resource-intensive testing requires explicit agreement, spending limits and stop conditions.
Supporting architecture and integrations
Identify relevant hosting, configuration, credential and third-party integration risks. Where necessary, combine the assessment with web application penetration testing, cloud penetration testing or an architecture security review.
ProCheckUp's generative AI testing experience
Our published engagement describes a penetration test of an internal generative AI application for a professional services consultancy. The assessment identified issues involving prompt injection, output handling, information disclosure and resource consumption.
Read the generative AI penetration-testing case study for the application context, findings and defensive recommendations. Published in March 2024, it records the models and implementation used at that time; a new assessment is scoped against your current deployment.
How an engagement works
Define the objective. Establish what the application does, who uses it, which information it can access and which outcomes matter to your organisation.
Agree the boundaries. Confirm written authorisation, systems and accounts in scope, third-party permissions, permitted techniques and escalation contacts.
Assess and validate. Apply relevant AI abuse scenarios alongside application testing, using controlled evidence to establish the impact of findings.
Report and prioritise. Explain the weaknesses, affected components and practical corrective actions.
Review remediation. Agree whether and how fixes will be retested, including any limits or changes in scope.
Relevant guidance includes the OWASP guidance for LLM applications and the UK AI Cyber Security Code of Practice. These help structure the discussion; the test plan should reflect the behaviour and architecture of your system rather than rely on a checklist alone.
Reporting and remediation
Agree the reporting requirements before testing so the findings support both security decisions and engineering work. The report should make clear:
The tested scope, access levels, assumptions and limitations.
The evidence supporting each finding and its impact in your environment.
Practical remediation recommendations and priorities.
Any scenarios that could not be completed or require further investigation.
The outcome of any separately agreed remediation verification.
A security assessment describes the system and scope tested at a point in time. Model, prompt, data and integration changes can affect subsequent behaviour; it does not certify that an AI system is free from all security, accuracy or ethical risks.
What to provide for scoping
A summary of the AI application, intended users and assessment objective.
Architecture and data-flow information, including hosting and model providers.
Details of retrieval sources, integrations, connected tools and user roles.
The available test environment, representative data and test accounts.
Relevant provider restrictions, operational limits and your preferred testing window.
Reporting requirements and the people responsible for remediation.
For an initial enquiry, a brief description of the environment and your timescale is sufficient. Do not include credentials or sensitive datasets in the contact form; agree an appropriate way to share assessment material during scoping.
AI security testing questions
Is AI penetration testing the same as testing with AI tools?
No. This service assesses the security of your AI-enabled application. Using AI tools to assist an ordinary penetration test is a separate question about how testing is delivered.
Does an ordinary web application test cover an LLM?
It can assess important parts of the surrounding application, but AI features introduce additional behaviour and trust boundaries. Agree AI-specific scope alongside relevant web, API and cloud testing.
Can you assess an application that uses a third-party model?
Our published engagement involved applications using hosted models. The assessment boundary must distinguish your implementation and authorised integrations from the provider's own infrastructure. Provider conditions and permissions are reviewed during scoping.
How long does an AI assessment take?
Duration depends on the application, user roles, integrations, access, permitted scenarios and reporting needs. Share those details so the engagement can be scoped; there is no single duration that suits every AI system.
Does testing provide AI compliance certification?
No. Technical testing can contribute evidence to a wider risk or assurance programme. It is not, by itself, certification of an AI management system or a determination of regulatory compliance.
Discuss your AI security assessment
Tell us what your AI application does, what it connects to and when you need assurance. Contact ProCheckUp to scope AI security testing, or call +44 (0)20 7612 7777.
Need Help?
If you have any questions about cyber security or would like a free consultation, don't hesitate to give us a call!
For More Information Please Contact Us
ACCREDITATIONS