Red teaming: test attack paths, detection and response
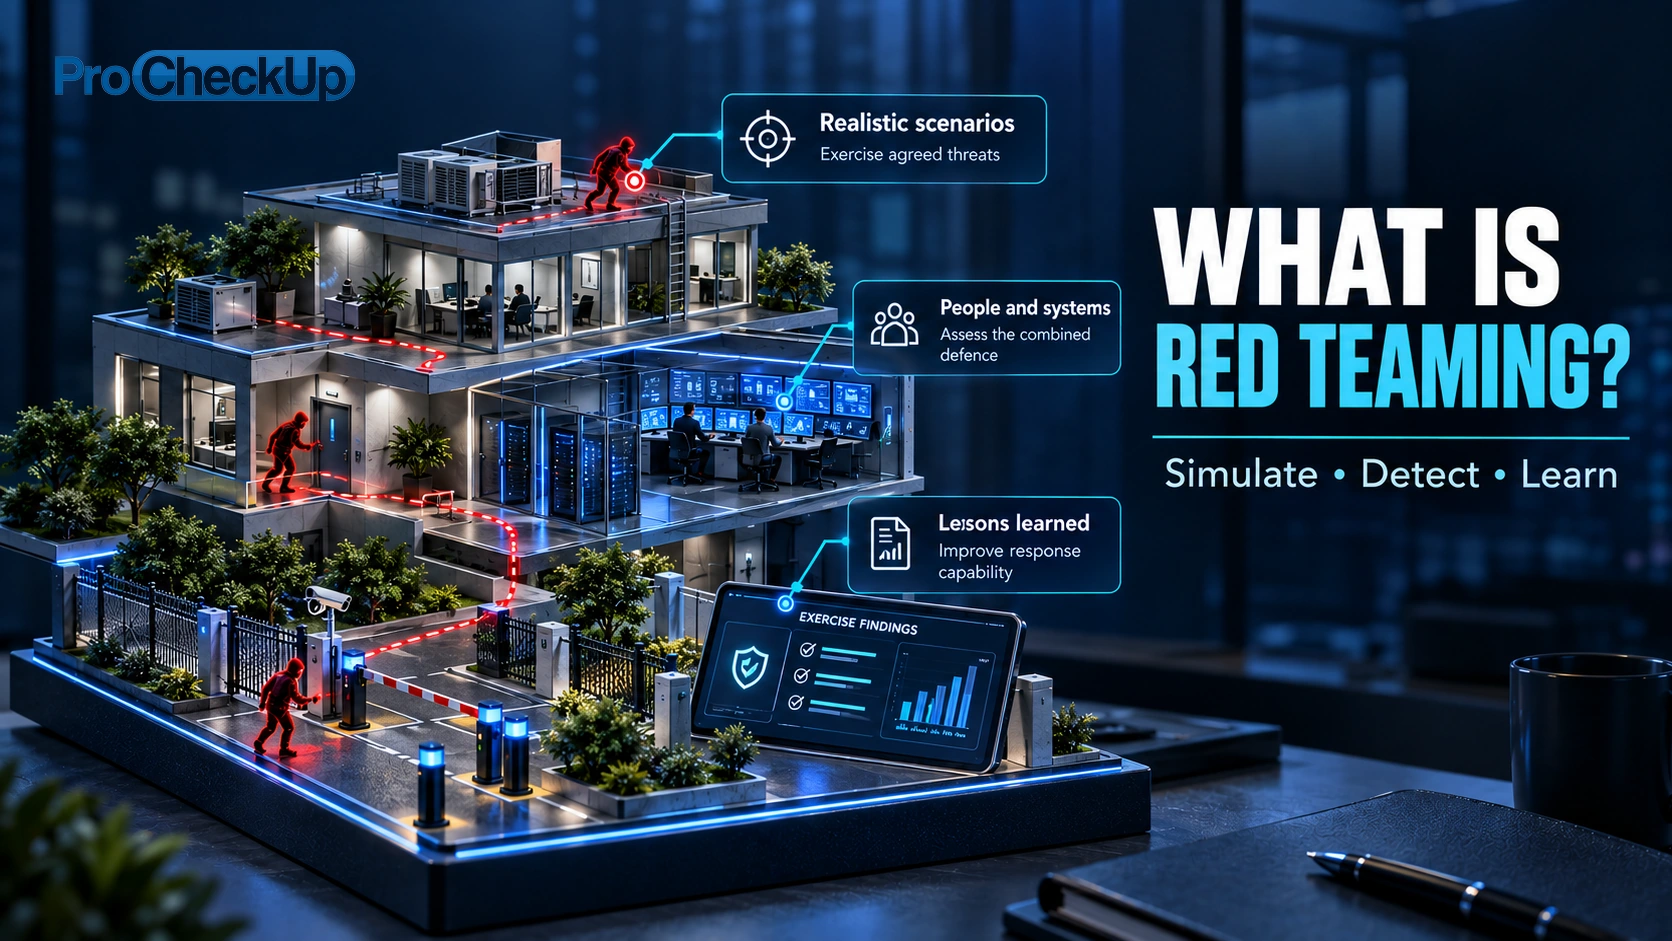
A red-team exercise is an authorised simulation of a realistic attack. It tests whether an attacker could achieve an agreed objective, and whether your people, processes and technology would prevent, detect and contain the activity.
A useful objective is specific: for example, whether an attacker could reach a synthetic payroll file from an agreed starting position. “Try to hack everything” is neither a safe scope nor a measurable outcome.
Reviewed: 27 October 2026.
Red, blue and purple teams
Red tests the attack path, blue defends, and purple describes their structured collaboration. A separate control group (sometimes called a white team) authorises and oversees the exercise, handles safety decisions and can stop it. Purple teaming does not require a permanently separate team.
| Approach | Purpose | When it is useful |
|---|---|---|
| Red team | Pursue an agreed adversary objective within defined rules. | You need evidence about attack paths and defensive response. |
| Blue team | Operate monitoring, investigation and response. | Everyday protection and detection; defenders participate in or learn from the exercise. |
| Purple teaming | Collaboratively test techniques, inspect telemetry and improve detections. | You want rapid, observable learning rather than a largely unannounced simulation. |
| Penetration test | Investigate exploitable weaknesses within a technical scope. | You need deeper assessment of a particular application, environment or release. |
Red and purple teaming are complementary ways of exercising capability. They do not imply a continuous managed detection service, a complete vulnerability inventory or independent certification.
What should a red-team exercise help you decide?
Start with a business question: could an attacker reach a sensitive service, change a protected record or interrupt an important process? Then agree a safe way to demonstrate the outcome. Access to a clearly marked test file can prove a path without taking real customer data.
- Prevention: which controls stopped progress, and which combination of weaknesses allowed it?
- Detection and response: did defenders see the activity, understand its significance and have authority to act?
- Improvement: which changes will reduce the business risk, who owns them and how will they be checked?
Success is useful evidence and improved capability. Reaching the target is not automatically a failure by the defenders; an early block is valuable evidence too. A time-limited exercise cannot prove that every possible attack would be stopped.
Are you ready for a red-team exercise?
Start with more focused testing or a collaborative exercise if basic asset ownership, patching, logging or incident contacts are missing. A sophisticated simulation can otherwise rediscover known weaknesses without producing actionable learning.
Readiness means there is a business sponsor, clear authority, a functioning response process and enough telemetry to examine what happened. It does not mean the organisation must already be highly mature.
- Identify the important service and a realistic attacker starting point.
- Check that test evidence can be safely separated from real customer data.
- Ensure someone can authorise urgent containment or stop the exercise.
- Confirm defenders’ logs will be retained long enough for analysis.
- Allocate time and owners for improvements and a follow-up exercise.

Choose realistic red-team scenarios
| Scenario | Question it can test | Boundary to agree |
|---|---|---|
| External entry | Can a realistic external starting point lead towards a defined business objective? | Permitted entry methods, time available and whether an assumed breach may be introduced if entry is not achieved. |
| Assumed compromised employee | Can ordinary access be contained before it reaches more sensitive systems? | Supplied account/device, permitted escalation and synthetic target data. |
| Supplier or cloud identity | Can third-party trust or cloud permissions lead to an important service? | Supplier authority, tenant boundaries and identities that may be used. |
| Physical or social engineering | Do entry, helpdesk or approval procedures resist a controlled deception? | Locations, people, privacy, safety, prohibited pretexts and immediate stop arrangements. |
| Threat-informed simulation | Can defenders recognise and respond to selected behaviours relevant to a credible threat? | Evidence supporting the scenario and the techniques actually exercised; do not imply an entire threat group has been reproduced. |
Methods such as network testing, application testing, wireless assessment and social engineering may support an objective. They are not all mandatory in every exercise. If the organisation primarily needs systematic assessment of an application’s features, commission the relevant focused test rather than assuming a red team will inspect them all.
Sector context changes the objective and constraints. A payment firm might protect a synthetic transaction approval; a hospital might exercise loss of a supporting service in a simulation; an industrial operator might test a remote-access boundary without interacting with live control equipment. These are illustrative planning choices, not permission to perform disruptive work.
Use MITRE ATT&CK adversary-emulation guidance to connect relevant threat intelligence to behaviours you can safely exercise. Record the selected techniques, available evidence and assumptions. Mapping a test to ATT&CK is a way to describe coverage; it is not certification or proof that every technique used by a threat actor was reproduced.
Advanced red-team scenarios
Advanced penetration-testing techniques can support a red-team objective, but the scenario should start with a business risk. The question is whether a realistic combination of access, permissions and human decisions could reach a protected service. Select the starting position and the defensive capability you need to examine.
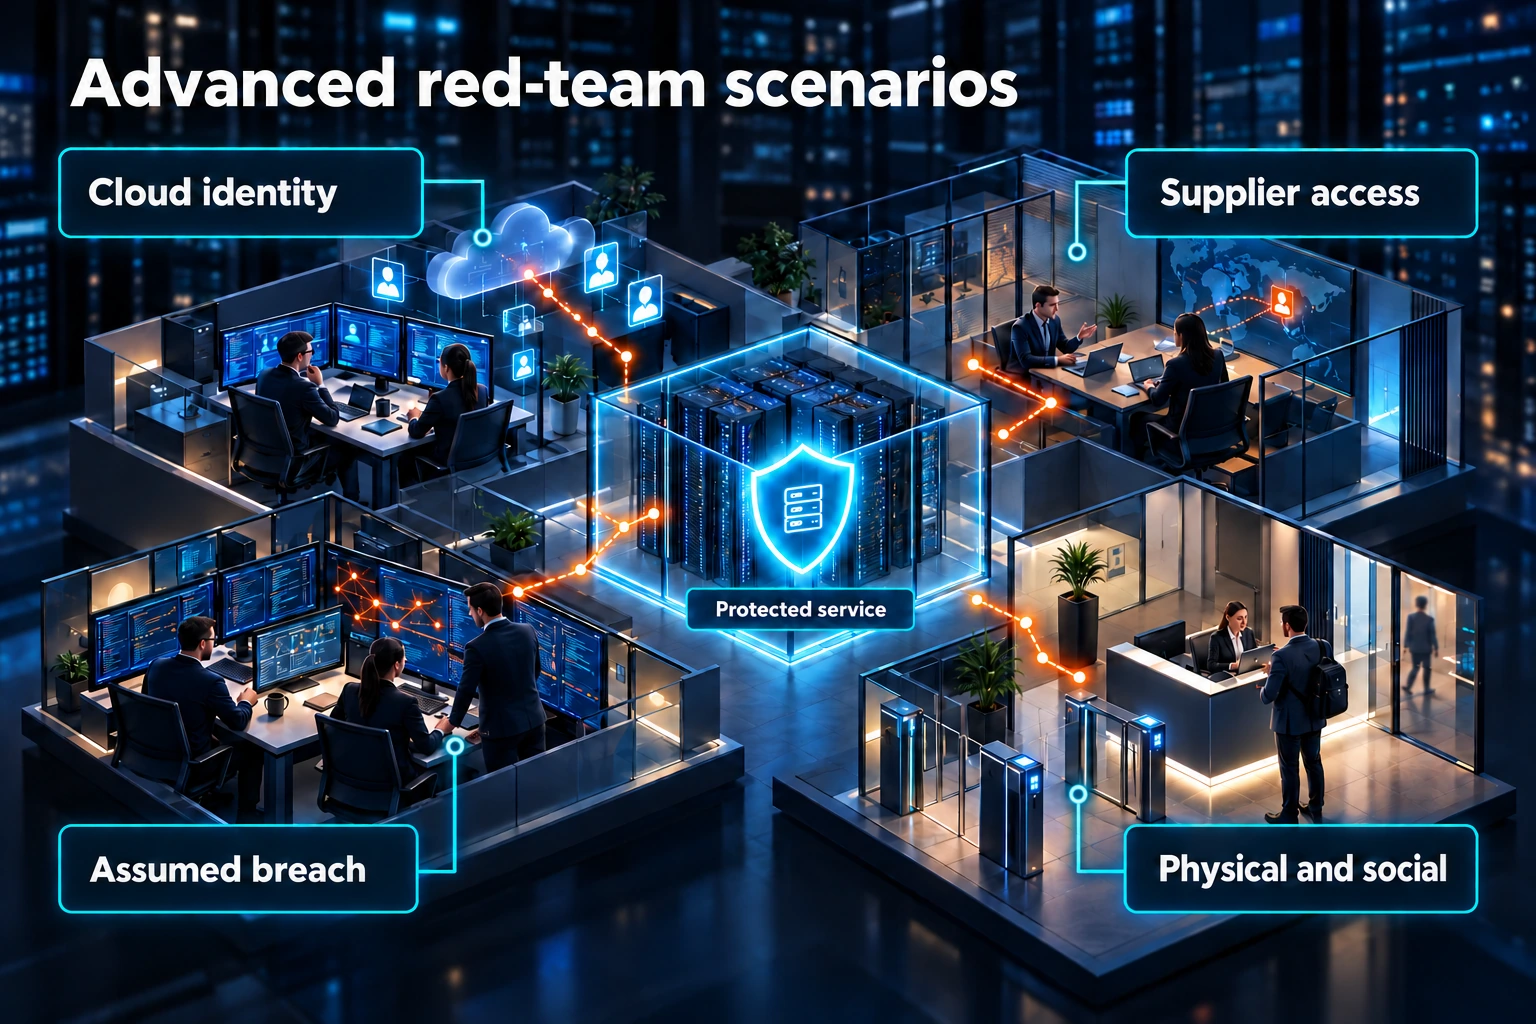
- Cloud identity: check whether an agreed test identity can reach sensitive resources, whether access restrictions hold and whether unusual activity is investigated.
- Supplier access: examine the permissions, ownership and monitoring of an authorised third-party access path. Obtain the relevant permissions before involving a supplier’s systems.
- Assumed breach: start with a supplied account or device to test the next defensive layer. Record the access provided so the result is not mistaken for a demonstrated external break-in.
- Physical and social: assess whether visitor, helpdesk or approval processes protect the same business objective and lead to an appropriate response.
For each selected scenario, record the permitted starting access, target service, safe proof of impact, expected observations and stop conditions. Connect the behaviours to relevant threat intelligence, as described in MITRE’s adversary-emulation guidance. Avoid adding techniques simply to make an exercise appear more advanced.
Physical access: test the whole response
A controlled physical-access scenario should examine what happens before, during and after an access request. Reaching a doorway alone says little about whether the organisation can recognise and handle suspicious activity. Assess the connection between people, access controls, monitoring and the authority to respond.
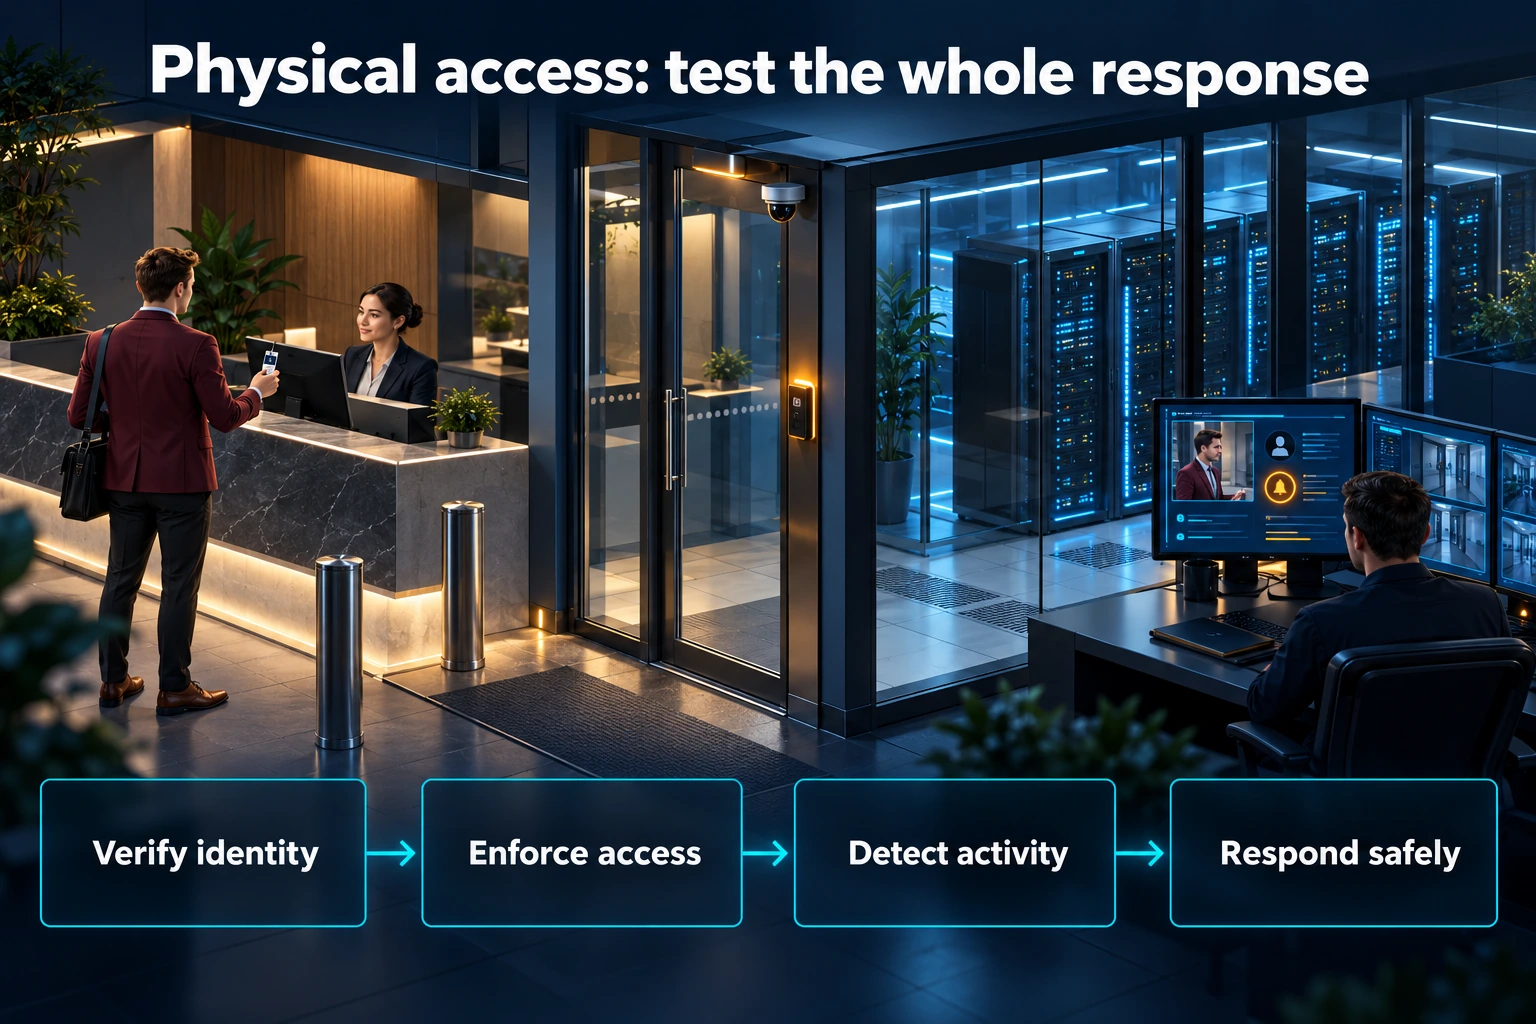
- Verify identity: does the agreed visitor request receive the required identity and sponsor checks, with a clear route for handling uncertainty?
- Enforce access: are access permissions limited to the authorised area, and are the relevant visitor and escort arrangements followed?
- Detect activity: do appropriate access events and observations reach the people responsible for reviewing them, with enough context to act?
- Respond safely: can staff escalate concerns, protect people and obtain a proportionate decision from the responsible owner?
Agree the premises, participants, time window, permitted interactions and privacy arrangements in writing. Name a control-group contact who can stop the activity immediately. Any test involving physical access needs the appropriate expertise and safety planning; a technical penetration-test scope does not automatically cover it. These planning considerations are reflected in the CREST red-team specialist syllabus.
Useful outcome: a receptionist correctly refuses an unverified request, but the concern is not passed to security. The exercise should record the successful identity check and the escalation gap, then assign and retest the process change. The aim is stronger controls and support for staff.
Agree the rules and protect operations
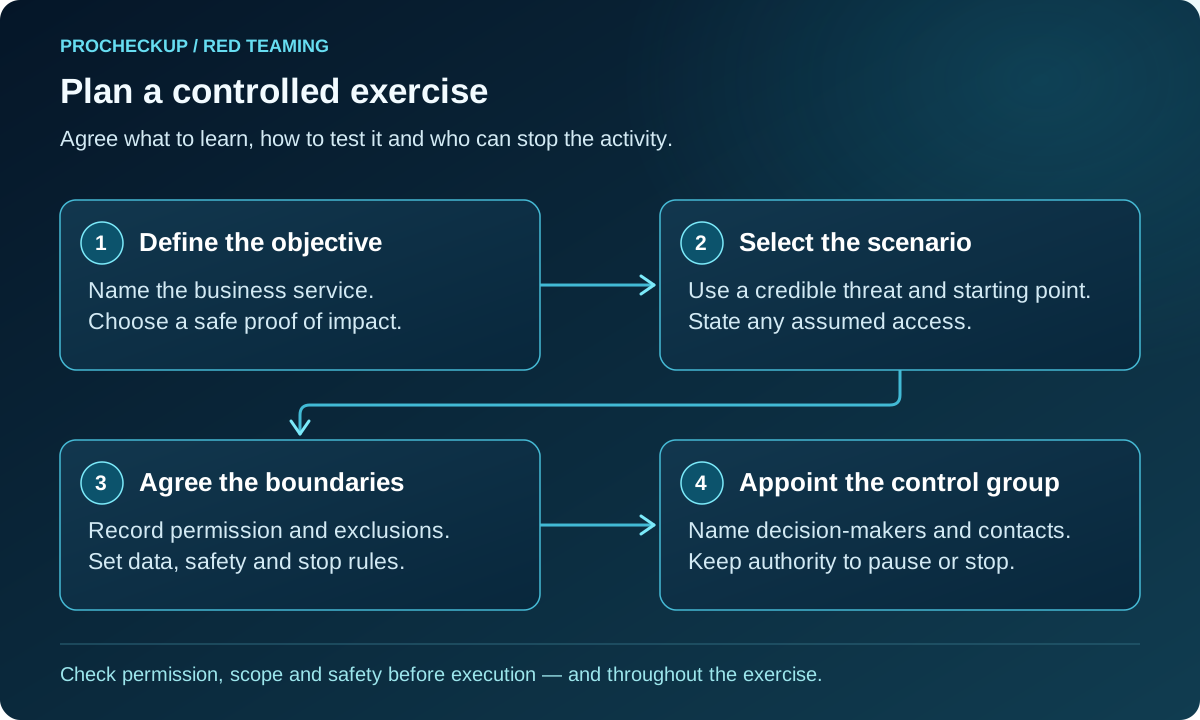
| Decision | Record before starting |
|---|---|
| Authority and scope | Entities, systems, people, premises, suppliers and dates covered by written permission. |
| Permitted techniques | Whether phishing, physical entry, credential attacks or simulated exfiltration are allowed, and explicit exclusions. |
| Safety | Protected systems, maximum impact, emergency contacts, stop conditions and restoration arrangements. |
| Control group | A small trusted group that knows the exercise and can distinguish it from a real incident. |
| Evidence and privacy | Use of synthetic data, minimal collection, access, retention and employee considerations. |
| Communication | Escalation of serious real weaknesses and how genuine incidents take precedence. |
Physical testing needs separate consideration of safety and premises authority. Social engineering should assess organisational controls fairly, not publicly shame individual staff. Any simulated data removal should use an agreed, safe marker or sample.
Keep a clear stop rule: if service health deteriorates, an unexpected sensitive system is reached or a genuine incident occurs, pause the affected activity and contact the control group. Record any approved change to scope before continuing. A supplier contract or permission from one business unit does not automatically authorise testing every connected service.
Run an exercise that produces usable evidence
Reconnaissance connects the agreed scenario to the real environment. The team may review permitted public information, exposed services and relevant organisational relationships to identify plausible entry opportunities. The rules of engagement should specify the permitted research, personal-data handling and any contact with people or suppliers. A discovered opportunity outside scope is raised with the control group before action. This phase helps explain which paths were explored, which were excluded and why.
Further guidance: CREST Certified Red Team Specialist syllabus v2.1.
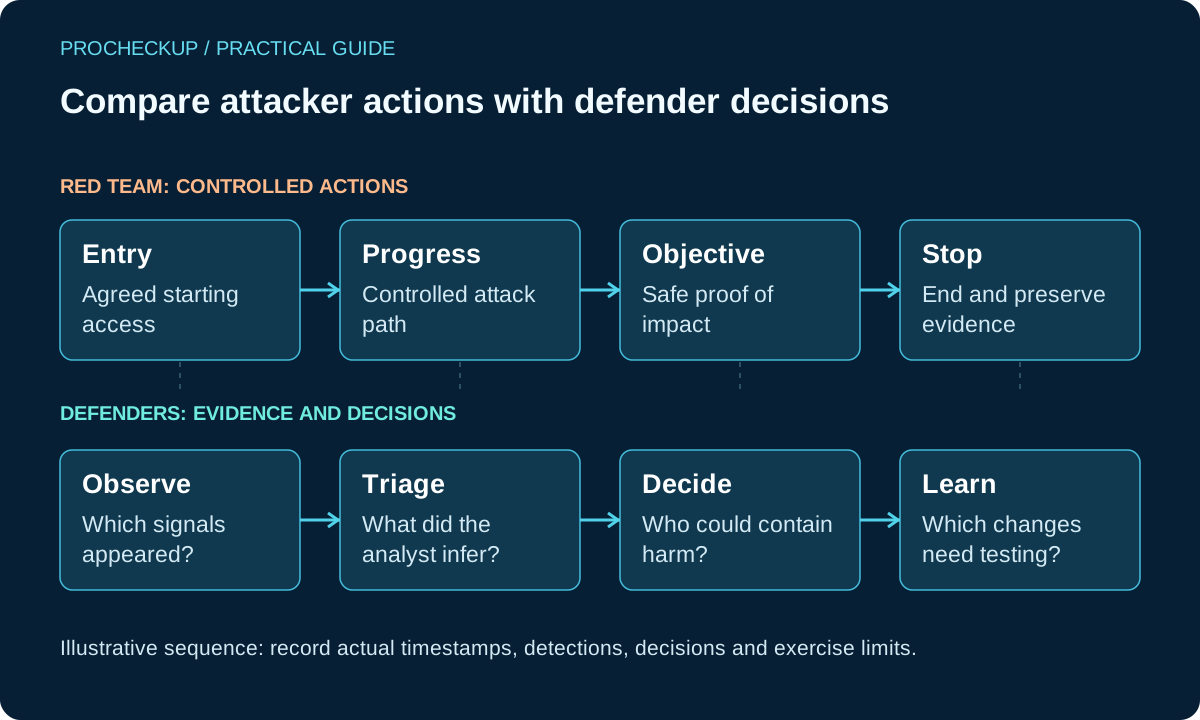
- Design: select a relevant scenario, assumptions and measurable decision points. Document any assumed breach or pre-positioned access.
- Execute: pursue the objective within the rules, keeping a timestamped record of actions and deviations.
- Reconstruct: compare the attack timeline with alerts, investigations and operational decisions. Identify telemetry that was missing or misleading.
- Improve: assign changes to preventive controls, detections, playbooks and authority to act.
- Validate: repeat selected techniques or use a collaborative session to demonstrate that the change works.
If entry is blocked, document the effective control. The control group may then authorise an assumed breach: a supplied account or access point that allows the next defensive layer to be examined. Label this clearly in the report; supplied access is not evidence that the team defeated the entry controls.
Measure decisions and coverage, not just compromise
| Measure | Useful interpretation |
|---|---|
| Prevented actions | Which barriers worked, under what assumptions, and whether the attacker changed path. |
| Detection | Which tested behaviours produced useful signals; elapsed time alone is not sufficient. |
| Investigation | Whether analysts identified affected assets, scope and business impact. |
| Response | Whether the right person could authorise effective containment without unnecessary disruption. |
| Recovery / lessons | Whether access was removed, changes were owned and specific weaknesses were retested. |
Avoid publishing a single “red-team score” as if it measures the whole organisation. Exercise duration, starting access, defender awareness and allowed techniques affect the result. Report those conditions alongside the findings.
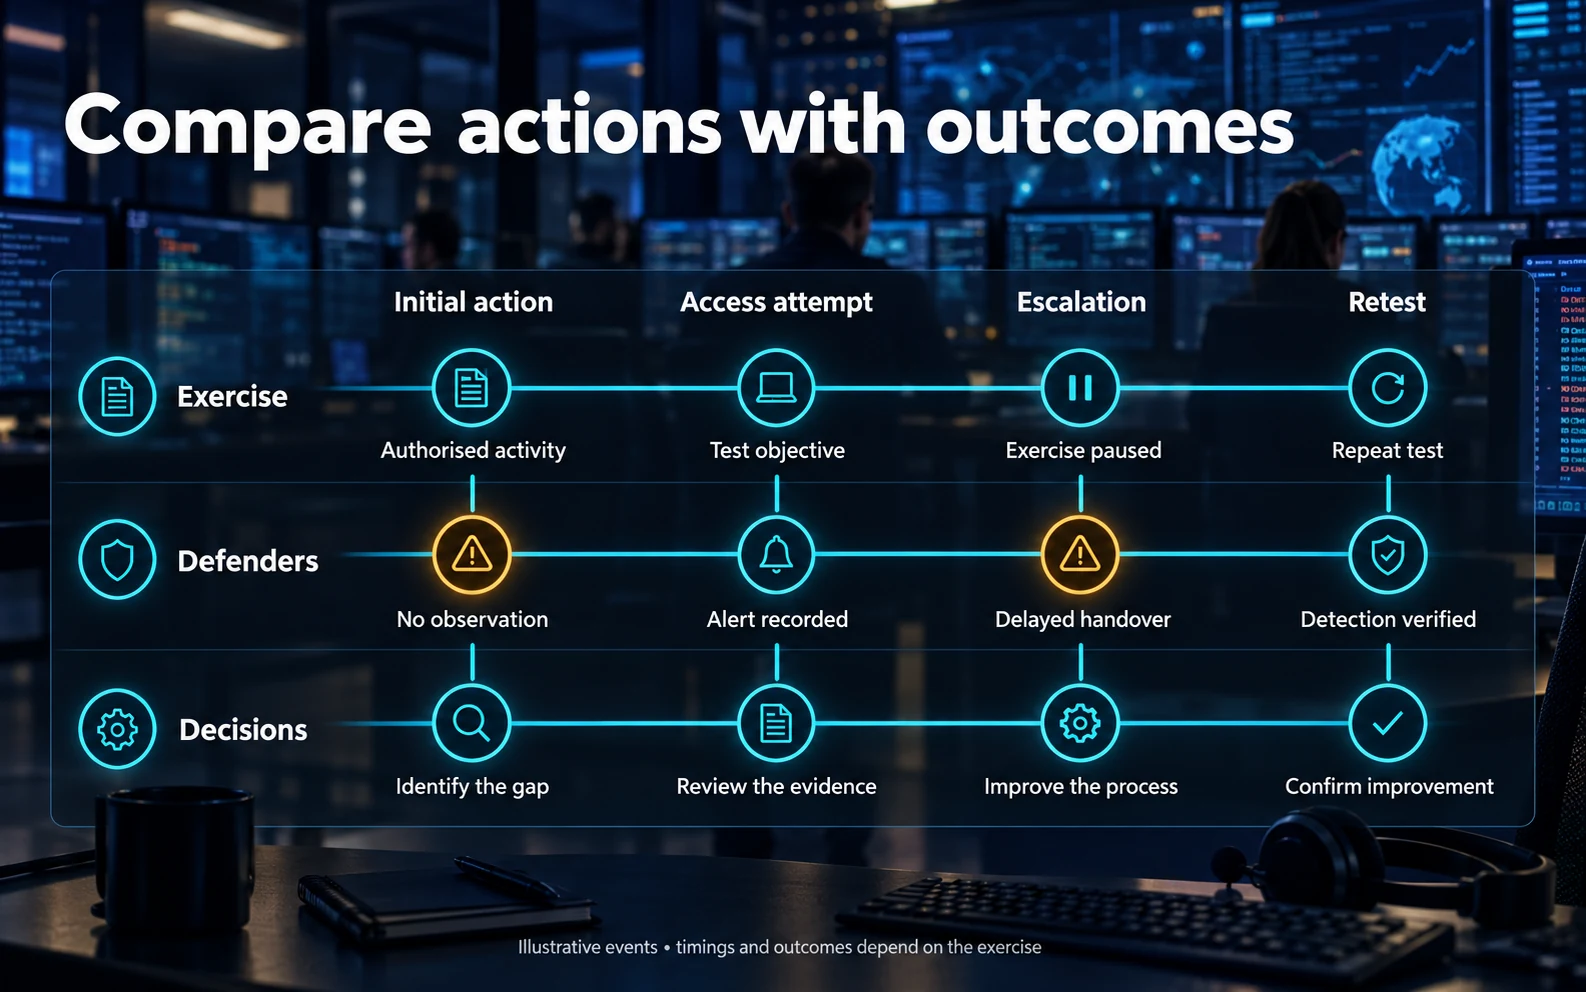
Define the clock before quoting timings. Record the tested action, first relevant telemetry, alert, analyst acknowledgement, escalation and containment. State the time zone, monitoring hours and any exercise pauses. Compare like-for-like events; a missing alert, an unread alert and an ineffective containment action need different fixes.
For example, CISA’s published red-team assessment describes both extensive attacker progress and an MFA barrier that prevented access to one sensitive business system. Reporting successful barriers alongside missed detections gives a more useful picture than a simple pass or fail.
Worked scenario: supplier access to a business service
An illustrative exercise starts with a simulated compromised supplier account. The objective is access to a synthetic file in a protected service. The team may test agreed access paths but must not interrupt production or collect real customer records.
A valuable finding might be that access was technically limited but an alert was not investigated because no team owned supplier activity. The improvement is then a combination of ownership, logging, alert context and a tested escalation route—not simply another security product.
The final report should show the path taken, failed attempts that demonstrate effective controls, observations from defenders, constraints and an achievable improvement plan.
Prepare the people, debrief and remove exercise access
The team needs technical skills appropriate to the scope and the ability to document decisions, handle sensitive evidence and communicate with the control group. Where physical or social methods are included, confirm relevant expertise rather than assuming technical testing experience alone is sufficient.
Agree how the control group will recognise genuine incidents and how exercise activity can be distinguished later without giving every defender the scenario in advance. Keep an action record and arrange a reliable stop channel. A real operational emergency takes priority over completion of the exercise.
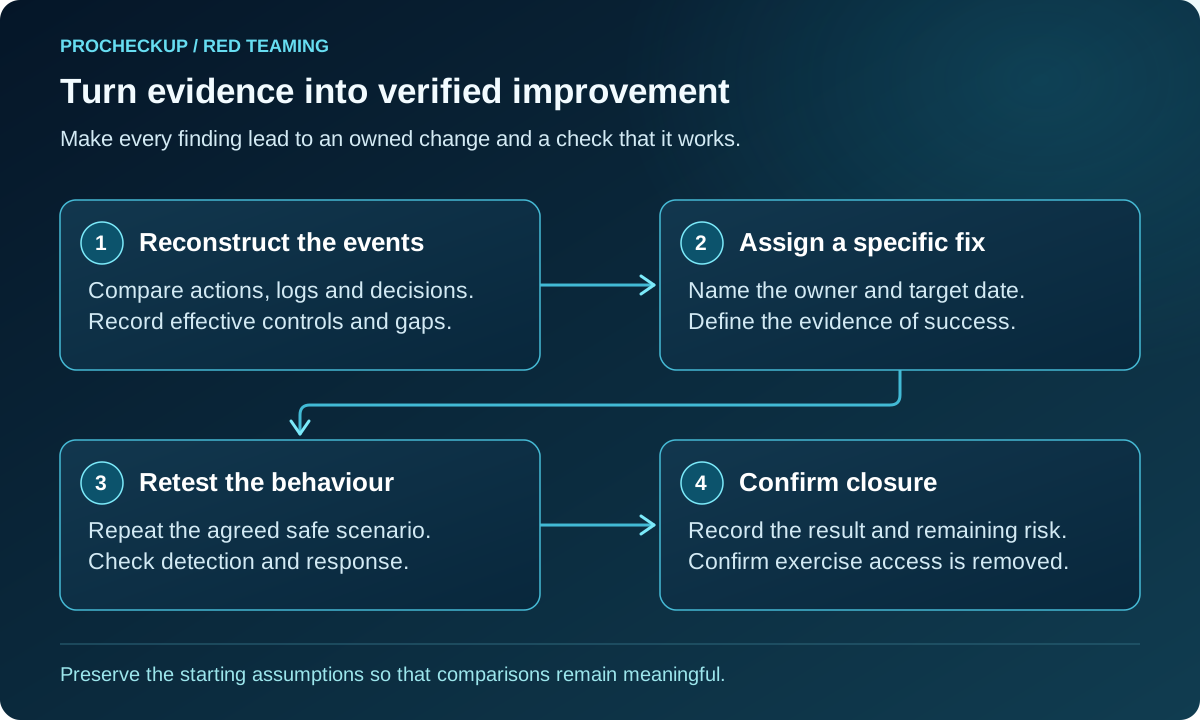
- Reconstruct the sequence jointly with defenders: what happened, what was logged, what was noticed and what decisions followed. Record successful controls as well as missed opportunities.
- Translate each weakness into a specific change, owner and verification method. Separate missing telemetry, unclear analyst context, ineffective response authority and preventive control failures.
- Remove test accounts, agreed persistence mechanisms, temporary rules and exercise data. Confirm cleanup with system owners rather than assuming it happened automatically.
- Run a targeted follow-up or purple-team session to check the improved behaviour. Preserve the starting assumptions so comparisons remain meaningful.
What should the report and follow-up contain?
Ask for an executive explanation of business impact and a technical record that defenders can use. Findings should distinguish demonstrated access, reasonable inference and activity that was not attempted. An untested route is not a verified weakness or a verified defence.
- Scope and limitations: objectives, permitted techniques, exclusions, dates, starting access and defender awareness.
- Evidence: a timestamped action and response timeline, affected assets, safe proof of impact and controls that worked.
- Action plan: a prioritised change, accountable owner, target date and verification method for each finding.
- Closure: confirmation that exercise access and data have been removed, plus retest evidence or an explicit record of the remaining risk.
For the supplier scenario above, an action might be: “Security operations owns the supplier-access alert; the identity team adds service-owner context; a follow-up test checks that the analyst identifies the account, escalates to the named owner and obtains the agreed containment decision.” Agree the response target with the service owner rather than using a universal time limit.
Common questions
Should defenders know the exercise is happening?
It depends on the learning objective. A trusted control group should always know. Wider awareness can be limited for a realistic response exercise or shared for collaborative improvement.
Is red teaming better than penetration testing?
They answer different questions. Use focused testing for technical coverage and an objective-led exercise for attack paths and response. Choose based on the assurance gap.
How often should we repeat it?
After meaningful changes or when improvements need validation, according to risk and applicable obligations. Repeating an unchanged scenario without addressing findings has limited value.
How long does it take and what affects the cost?
There is no single useful duration or price. Threat research, the number of objectives, technical and physical locations, access constraints, evidence analysis and retesting all affect effort. Ask the proposal to separate preparation, execution, debriefing and follow-up, and state what happens if the first entry route is blocked.
Does a red-team exercise demonstrate regulatory compliance?
It can provide evidence for an assurance programme, but a general commercial exercise does not automatically satisfy a regulated testing framework. Where CBEST applies, follow its specific governance, scope, provider, reporting and supervisory requirements. Confirm the applicable framework before commissioning.
How do we choose a suitable provider?
Check experience with the proposed environment, relevant qualifications and any required provider accreditation. Ask for an anonymised example report, the safety and escalation process, how sensitive evidence is protected, and whether the quoted work includes a joint debrief, cleanup and retesting. A technical certificate alone does not demonstrate competence in every physical, social or operational scenario.
Can automated tools or AI replace the exercise?
Automation can help repeat selected behaviours and compare detections. It does not, by itself, reproduce the judgement, business context or safety decisions of an objective-led exercise. Check which behaviours and systems were actually tested, how results were validated and which human decisions remain outside the assessment.
Related guidance
Scope a penetration test · Plan safe social-engineering assessment · Prioritise capability improvements
Use the NCSC Cyber Assessment Framework as a source of outcome-based questions about prevention, detection and response where relevant; it is not a red-team certification scheme.
Discuss a red-team engagement.
Further reading: CREST’s guide to penetration testing explains the relationship between focused testing and objective-led red teaming. The planning and follow-up checklists above are practical recommendations, not a substitute for a scheme’s own requirements.
Need Help?
If you have any questions about cyber security or would like a free consultation, don't hesitate to give us a call!
For More Information Please Contact Us
ACCREDITATIONS