Twelve practical steps for UK data protection
Use this guide to turn data-protection obligations into owned, reviewable work. Begin with what personal data you use, why you need it and what could happen to the people concerned. Security controls are essential, but data protection also covers fairness, transparency, lawful use and individual rights.
This guide focuses on the UK. The Data (Use and Access) Act 2025 amends the UK GDPR, Data Protection Act 2018 and PECR rather than replacing them. The ICO confirmed in June 2026 that its data-protection provisions were in force. Check the rules applying to your particular processing and any other jurisdictions. ICO: changes for organisations.
Reviewed: 26 October 2026.
1. Assign responsibility and build awareness
Give senior management a clear view of the personal data used, significant risks and unresolved decisions. Train people on the tasks they actually perform: recognising a rights request, sharing information safely or escalating an incident.
Owner: a senior accountable sponsor with privacy and operational leads. Evidence: responsibilities, role-specific training and an action register. Review: after organisational changes and when incidents reveal a gap.
2. Locate personal data and map its use
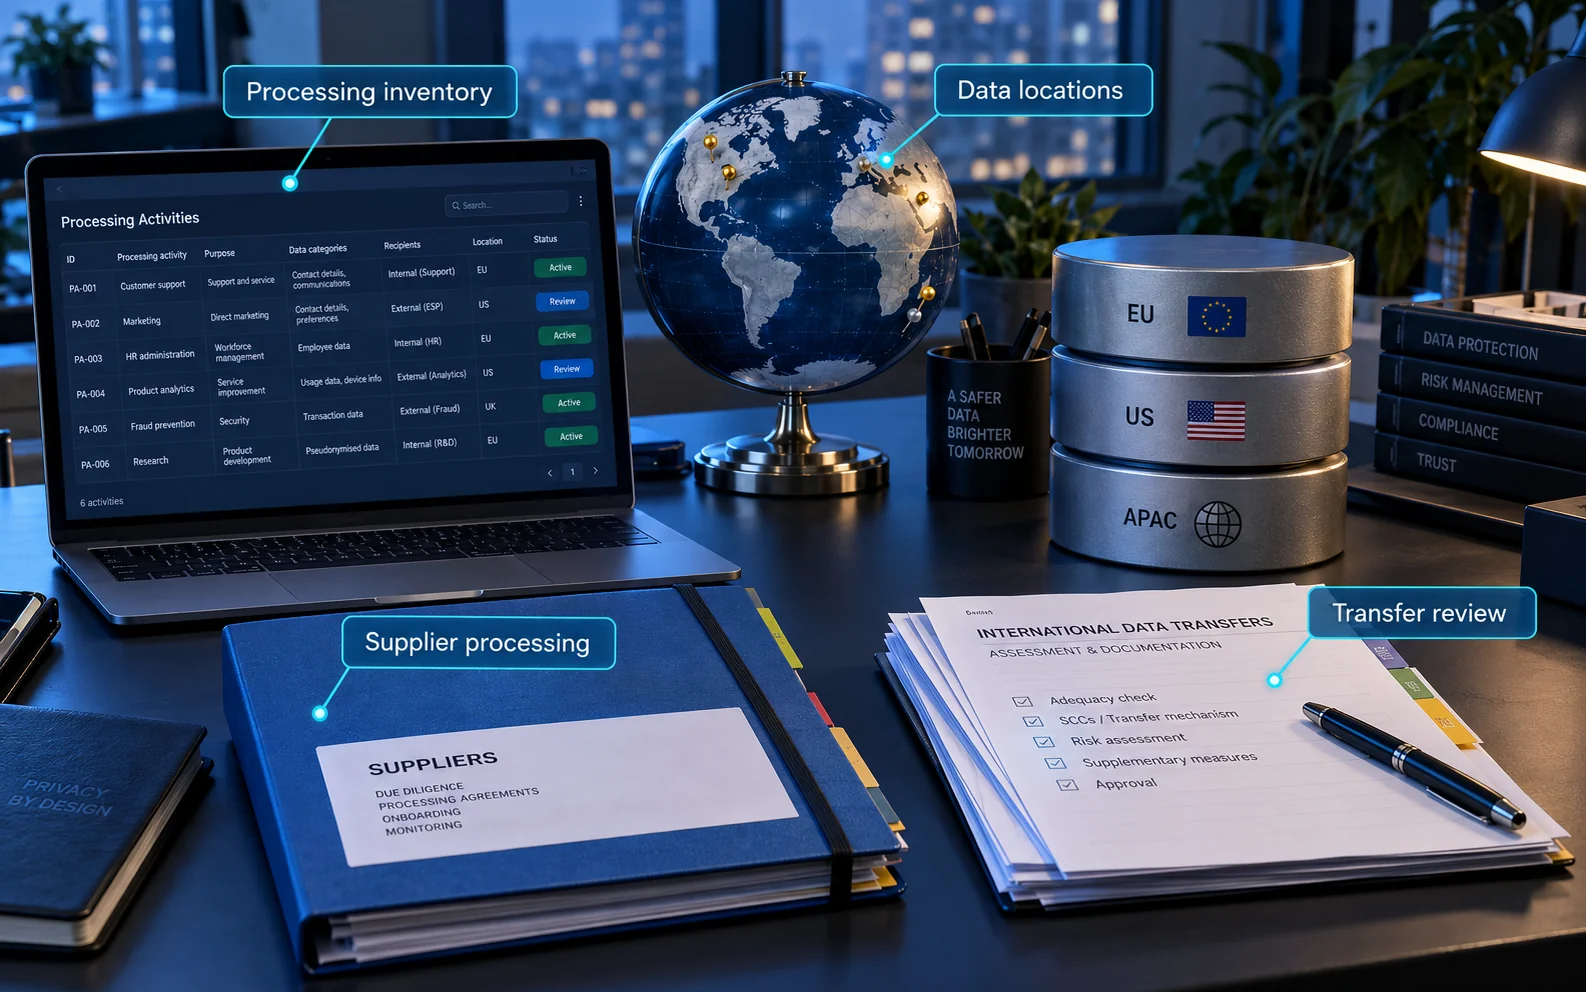
Record data categories, people affected, purposes, sources, recipients, systems, retention and international access. Include email, exports, backups and suppliers, not just the main database. Decide whether you act as controller, processor or both for each activity.
Owner: business data owners supported by IT and privacy. Evidence: an accurate processing inventory and data-flow map, with records required by the applicable law. Review: when a process, supplier or purpose changes.
3. Make notices and internal policies match reality
Tell people clearly what you do with their information, why, who receives it, how long it is retained and how to exercise their rights. Internal procedures should support that explanation. A copied privacy notice cannot correct an undisclosed use of data.
Owner: privacy and service owners. Evidence: versioned notices, retention decisions and checks against actual processing. Review: before introducing a new use or materially changing the service.
4. Enable rights and handle complaints
Create a route for requests concerning access, correction, erasure, restriction, objection and portability where applicable. These rights have conditions and exceptions; do not promise automatic deletion of every record. Review safeguards for significant automated decisions, including human intervention where required.
Direct marketing is an important exception to the general qualifications above. If someone objects to the use of their personal information for direct marketing, stop using it for that purpose, including associated profiling. Record and apply the preference across relevant systems and suppliers. An objection can be verbal or written.
Do not simply delete the contact and then re-import it in a later campaign. Retain only the information needed on a controlled suppression list to respect the objection. This is different from keeping the person’s information for marketing, and does not automatically require deletion of records legitimately needed for other purposes.
Further guidance: ICO: Respect people's preferences; ICO: Right to object—updated 23 July 2026.
The current UK complaints duty requires an accessible route, acknowledgement within 30 days, appropriate investigation and an outcome without undue delay. Keep the person informed. A complaints acknowledgement deadline is separate from a subject access deadline. ICO complaints guidance.
Owner: privacy lead and customer-facing teams. Evidence: request and complaint logs, decisions, communications and escalation. Review: recurring causes and missed deadlines.
5. Be ready for subject access requests
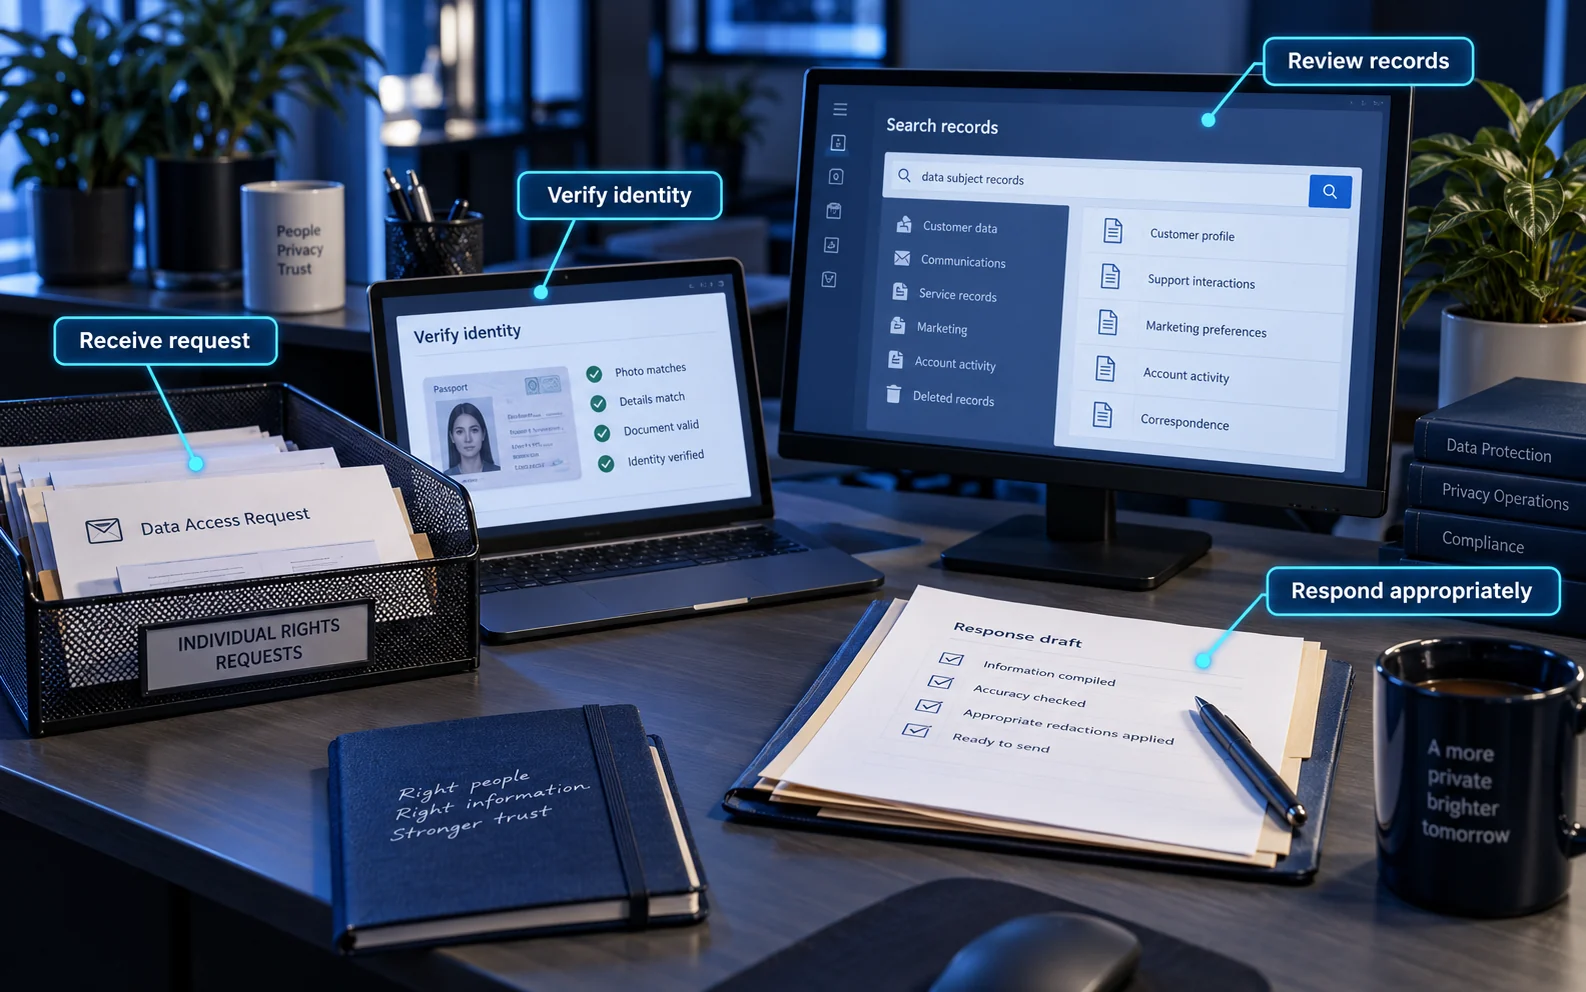
Recognise requests made verbally or in writing; people do not need to use a special form. Respond without undue delay and normally within one month. A necessary extension of up to two further months is possible for complex or multiple requests, with the required explanation within the initial month. Apply identity and clarification rules correctly rather than pausing routinely.
Search reasonably and proportionately, consider applicable exemptions and other people’s information, and provide the response securely. Most requests cannot be charged for. ICO subject access guide.
Owner: a request coordinator and relevant data owners. Evidence: receipt date, searches, deadline calculation, redaction decisions and delivery. Review: after each difficult request.
6. Identify a lawful basis for each purpose
Choose and document the applicable lawful basis before processing. Consent is one possible basis, not a universal requirement. Contract, legal obligation and other bases have specific conditions. Special-category information also needs an additional condition, and criminal-offence information has separate requirements.
The newer recognised-legitimate-interests basis is limited to specified purposes; it is not a general exemption from assessing lawful use. Do not retrospectively choose a convenient basis to justify an activity already underway.
Owner: the business purpose owner with privacy advice. Evidence: purpose-to-basis mapping and any required assessments or conditions. Review: before changing the purpose.
7. Use and record consent properly
Where relying on consent, ensure it is freely given, specific, informed and unambiguous, with an appropriate affirmative action. Keep evidence of what the person agreed to and make withdrawal as easy as giving consent. Do not bundle unnecessary processing into a service as a condition without considering validity.
Electronic marketing and cookies also involve PECR. Some exemptions exist, including changes under the 2025 Act, but this does not make every analytics or advertising use exempt from consent. Assess the particular technology and purpose.
Owner: marketing and product owners with privacy support. Evidence: consent wording, records, preference handling and technology assessment. Review: new campaigns, tags and vendors.
8. Protect children’s information
Consider children’s interests, understandable explanations, age-appropriate design and risks from profiling or disclosure. The UK threshold of 13 is specifically relevant when relying on consent to offer an information society service directly to a child. Below that age, obtain and reasonably verify parental authorisation where that rule applies. It is not a blanket rule requiring parental consent for all processing involving children. ICO guidance on children and lawful basis.
Owner: product/service owner with safeguarding and privacy input. Evidence: age-related risk assessment and design decisions. Review: changes to likely users, features and data sharing.
9. Prepare for personal data breaches
A personal data breach can involve loss of availability or integrity as well as unauthorised disclosure. Contain the incident, establish facts and assess the risk to people. Notify the ICO without undue delay and within 72 hours of awareness where feasible, unless the breach is unlikely to result in a risk to rights and freedoms. Explain delays and provide information in phases if necessary.
Tell affected people without undue delay where the breach is likely to create a high risk, subject to applicable exceptions. A processor must notify its controller without undue delay. Record all personal data breaches and the reasoning behind notification decisions. ICO breach guidance.
Owner: incident lead and privacy decision-maker. Evidence: timeline, risk assessment, decisions and communications. Review: exercise the plan and learn from incidents.
10. Use DPIAs and privacy by design
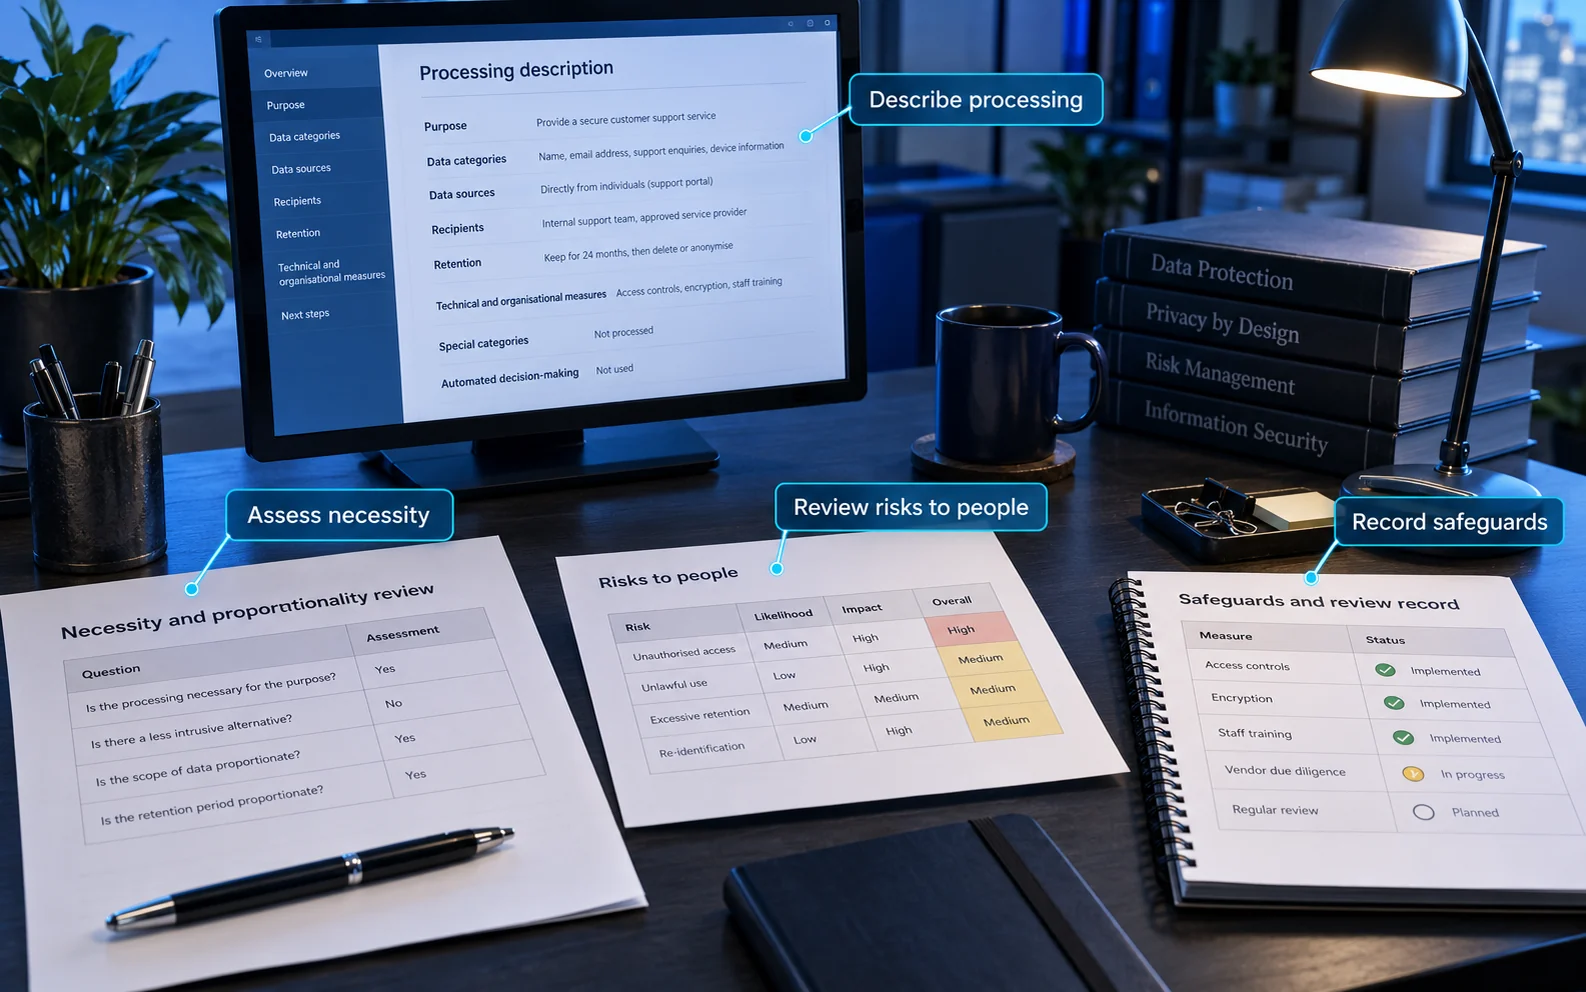
Assess privacy early when designing or changing processing. A data protection impact assessment is required where processing is likely to result in high risk to people. Explain necessity, proportionality, risks and safeguards; consult the DPO where appointed and the people affected where appropriate. If high residual risk cannot be reduced, consider the requirement to consult the ICO before starting.
Owner: project sponsor with privacy and technical contributors. Evidence: DPIA, decisions and implemented safeguards. Review: before launch and when risks or processing change. ICO DPIA guidance.
11. Decide whether a DPO is required
Assess the statutory criteria, including relevant public authorities, core activities involving large-scale regular and systematic monitoring, or large-scale processing of special-category or criminal-offence data. A DPO is not mandatory for every small business.
Where appointed, provide expertise, resources, independence and access to senior management, and avoid conflicting duties. Even without a mandatory DPO, assign responsibility for privacy decisions.
Owner: senior management. Evidence: the appointment decision, role and reporting arrangements. Review: material changes in processing or scale. ICO DPO guidance.
12. Check suppliers and international transfers
Assess territorial scope from the organisation’s activities and legal criteria, not just a person’s citizenship. Map overseas recipients and remote access as well as storage locations. Determine whether an arrangement is a restricted transfer and identify a valid adequacy arrangement, appropriate safeguard or applicable exception.
Review processor terms, subprocessors, security, deletion and breach notification. A supplier’s marketing claim of “GDPR compliant” is not sufficient evidence of your own compliance.
Owner: procurement, legal/privacy and the service owner. Evidence: due diligence, contracts, transfer assessment and review dates. Review: supplier, destination or legal changes. ICO international transfer guidance.
Worked example: connect a data map to notices, rights and retention
Consider an illustrative recruitment process: an applicant submits a CV through a hosted form; HR and the hiring manager review it; a screening supplier receives selected information; records are retained or deleted after a defined period. Map the actual transfers and copies, including emailed attachments and exported spreadsheets, rather than recording only the name of the recruitment platform.
| Question | What the process owner should record |
|---|---|
| Why is each item collected? | The recruitment purpose, necessity and chosen lawful basis; any separate purpose needs its own assessment. |
| Who decides and who acts on instructions? | The organisation’s and suppliers’ roles for the particular processing, with responsibilities documented. |
| What does the applicant need to know? | Clear privacy information matching the actual recipients, uses, retention and rights routes. |
| Where can a rights request reach? | A workable search across the platform, HR records and relevant suppliers, with identity and disclosure checks. |
| When does information leave the process? | A justified retention schedule, deletion procedure and handling of remaining backup copies under controlled arrangements. |
Follow the same record when testing access, correction, a supplier change or a suspected disclosure. It exposes gaps that a policy review alone can miss. Use ICO documentation guidance to establish applicable recording duties and distinguish a practical data map from any formal record required by law. This example does not prescribe a lawful basis or retention period for every recruitment process.
Make the twelve steps an ongoing programme
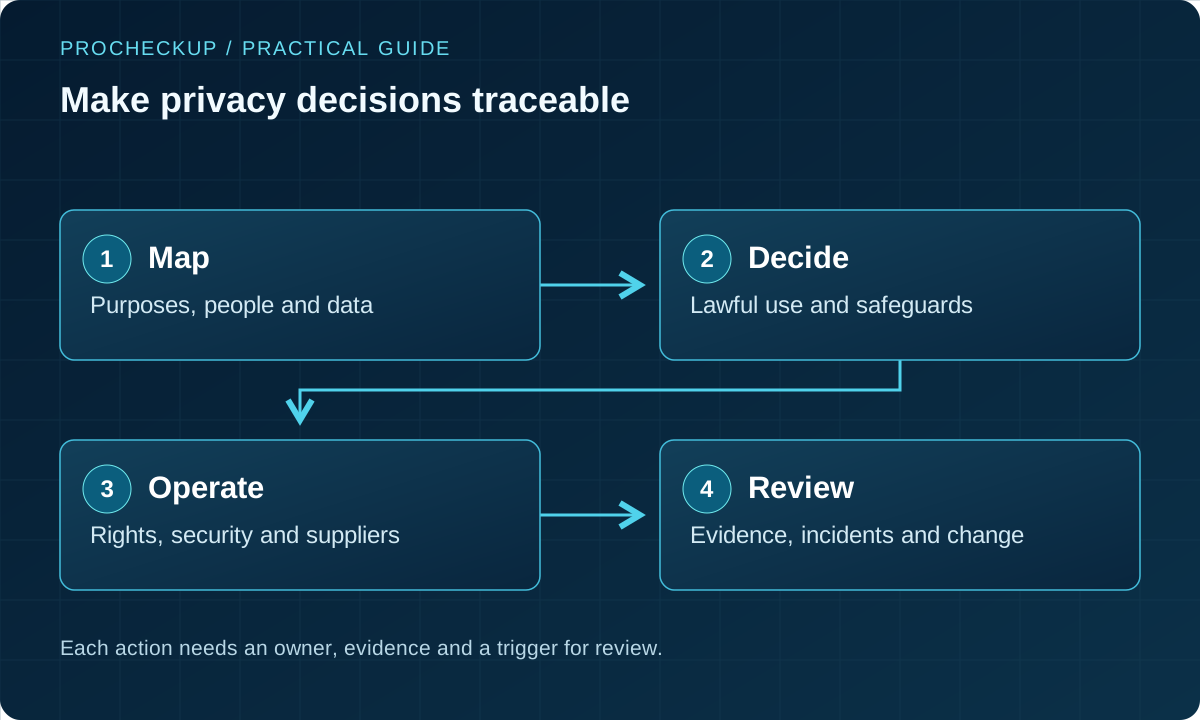
For a first review, select one important process such as recruitment or customer onboarding. Trace it end to end, compare the notice with reality, test a rights request and confirm deletion and incident escalation. Use the findings to improve the wider programme.
For support with high-risk processing, see our DPIA service. The guide is an implementation aid; apply the detailed legal conditions to your actual processing.
Need Help?
If you have any questions about cyber security or would like a free consultation, don't hesitate to give us a call!
For More Information Please Contact Us
ACCREDITATIONS