Cyber maturity assessment: turn evidence into a practical roadmap
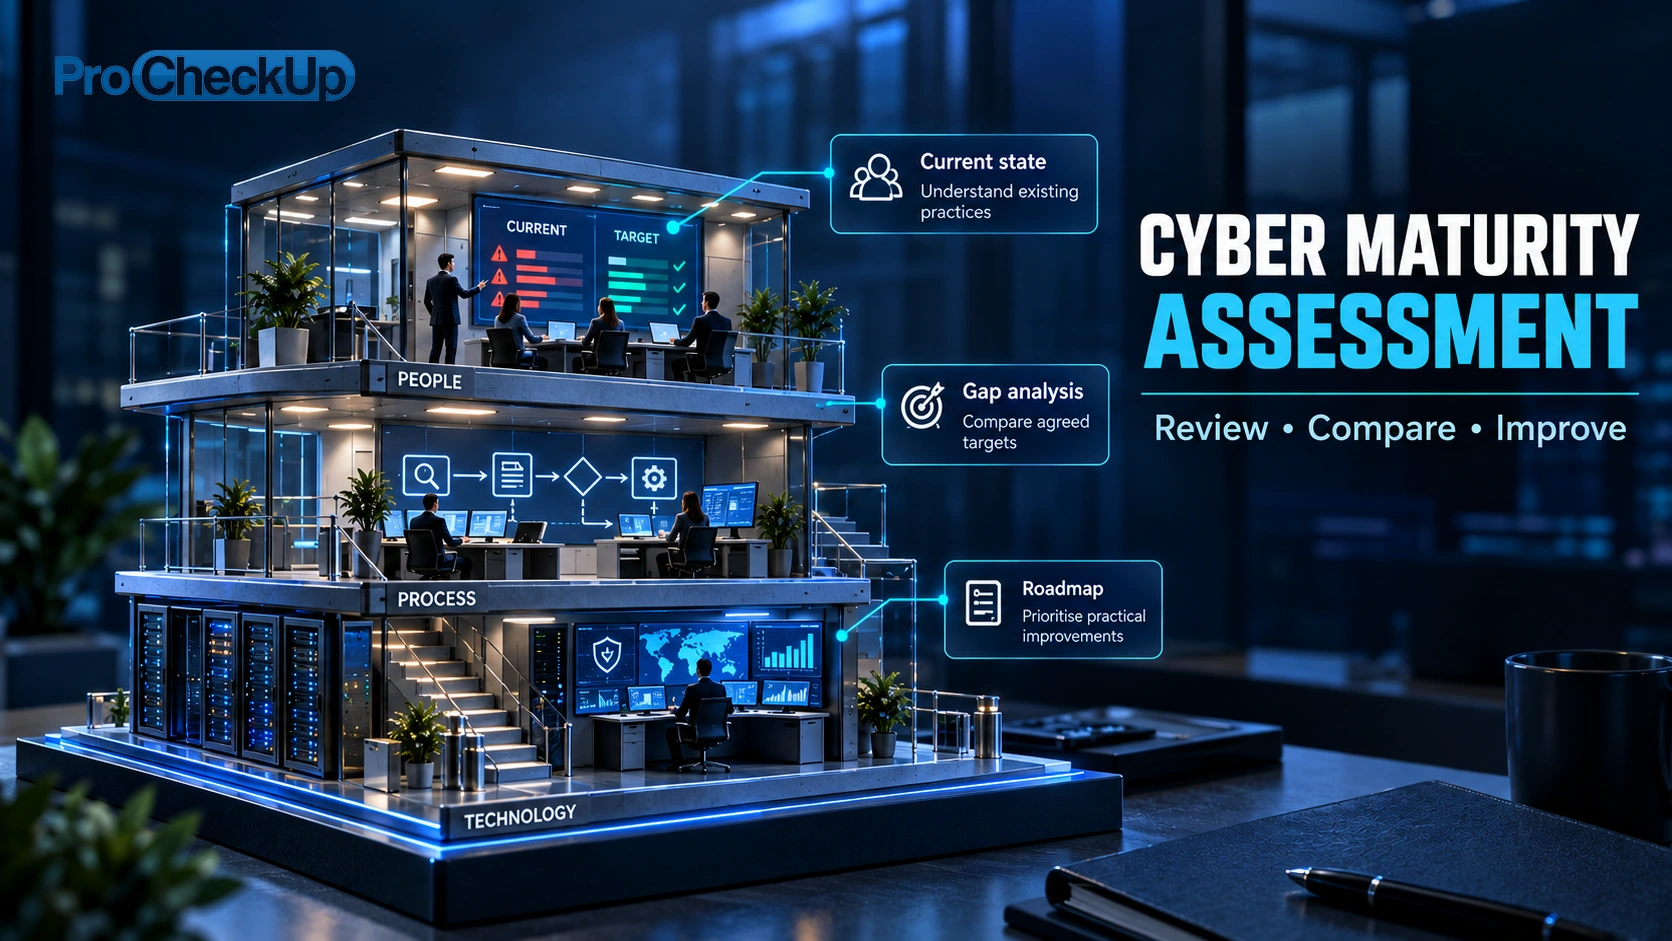
A cyber maturity assessment examines how consistently an organisation manages security and whether its capabilities fit its business needs. It should explain what works, where evidence is weak and which improvements deserve attention first.
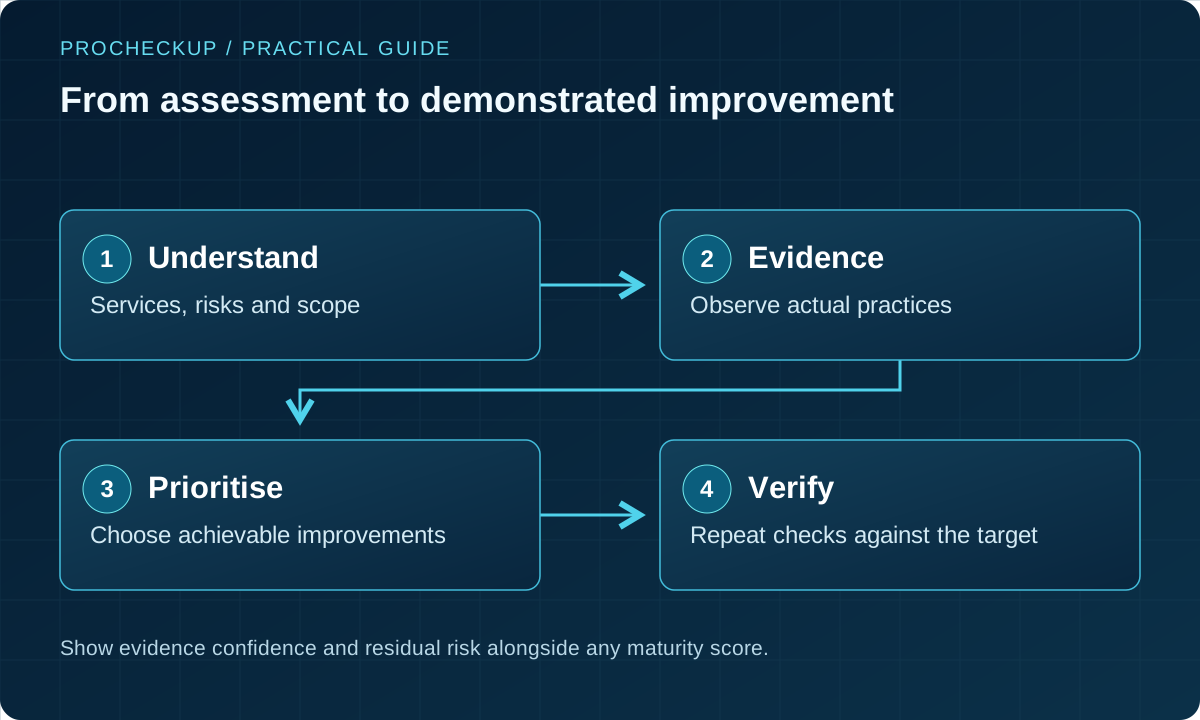
A useful result is an achievable roadmap with owners and verification steps—not just a score or a long list of products. Begin with the services the organisation must deliver and the consequences of disruption or misuse.
Reviewed: 26 October 2026.
Maturity, risk, compliance and testing answer different questions
| Assessment | Main question | Limit |
|---|---|---|
| Maturity | How repeatable and effective are our security practices? | A capability score is not a prediction of every attack. |
| Risk | What could happen, how would it affect us and what should we do? | Risk estimates depend on assumptions and available evidence. |
| Compliance | Do we meet specified obligations in the assessed scope? | Meeting a requirement does not address every business risk. |
| Penetration testing | Can weaknesses be exploited within an agreed technical scope? | A test samples systems and paths at a point in time. |
Combine the approaches where useful. A maturity review can identify a weak access-review process; a technical test can then examine whether the weakness exposes a critical service.
Agree scope and the decisions the assessment must support
Identify business services, locations, technology, suppliers and relevant obligations. Decide whether the review covers the whole organisation or a defined part. Record exclusions and the period represented by the evidence.
Agree the framework, scoring definitions and target-setting method before interviews. The assessment should be proportionate to the organisation’s size, risk and resources. A small business does not need every practice expected of a large regulated operator.
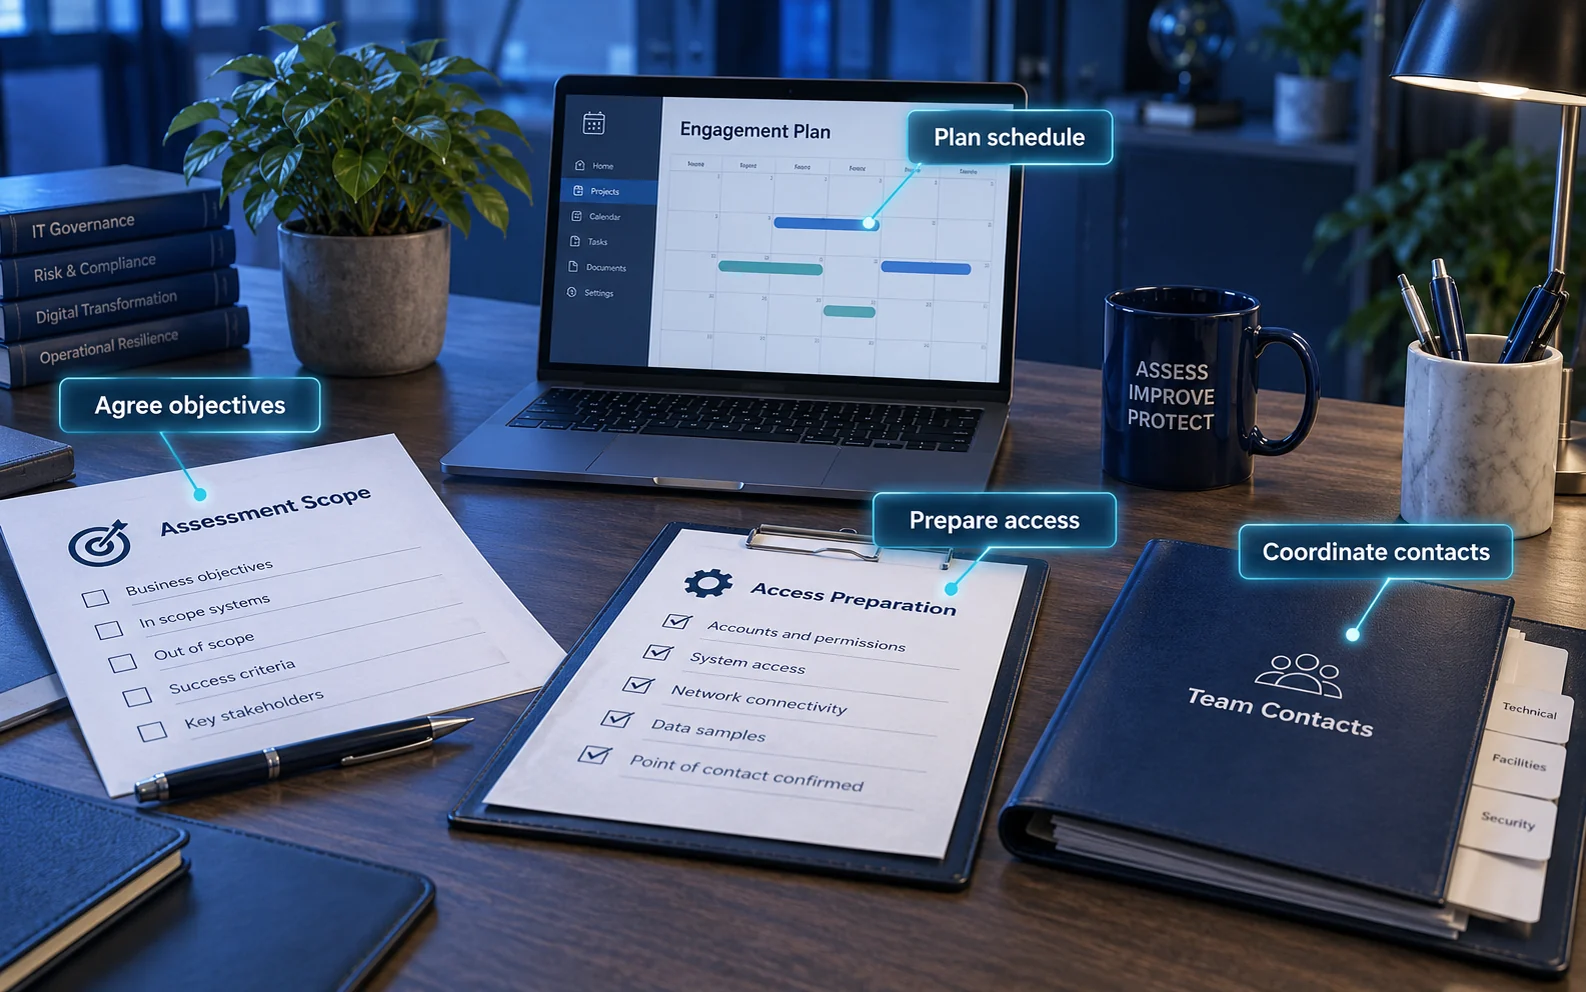
- What needs to keep working, and for how long can it be unavailable?
- Which information, identities and suppliers does that service depend on?
- Who owns security decisions and accepts residual risk?
- Which recent changes, incidents or audit findings should influence the review?
Use a framework without overstating what it proves
NIST CSF 2.0 organises cybersecurity outcomes under six functions: Govern, Identify, Protect, Detect, Respond and Recover. Current and target profiles help describe relevant outcomes. It is not a product certification or a prescribed maturity-scoring system. Its Implementation Tiers should not be relabelled as a generic five-point maturity scale. NIST CSF FAQs.
Other frameworks may be suitable for specific sectors or obligations. Explain why a framework was selected, how findings map to it and where the assessment uses its own scoring rubric. Avoid claiming that one score demonstrates compliance with every referenced standard.
Assess practice, not just documents
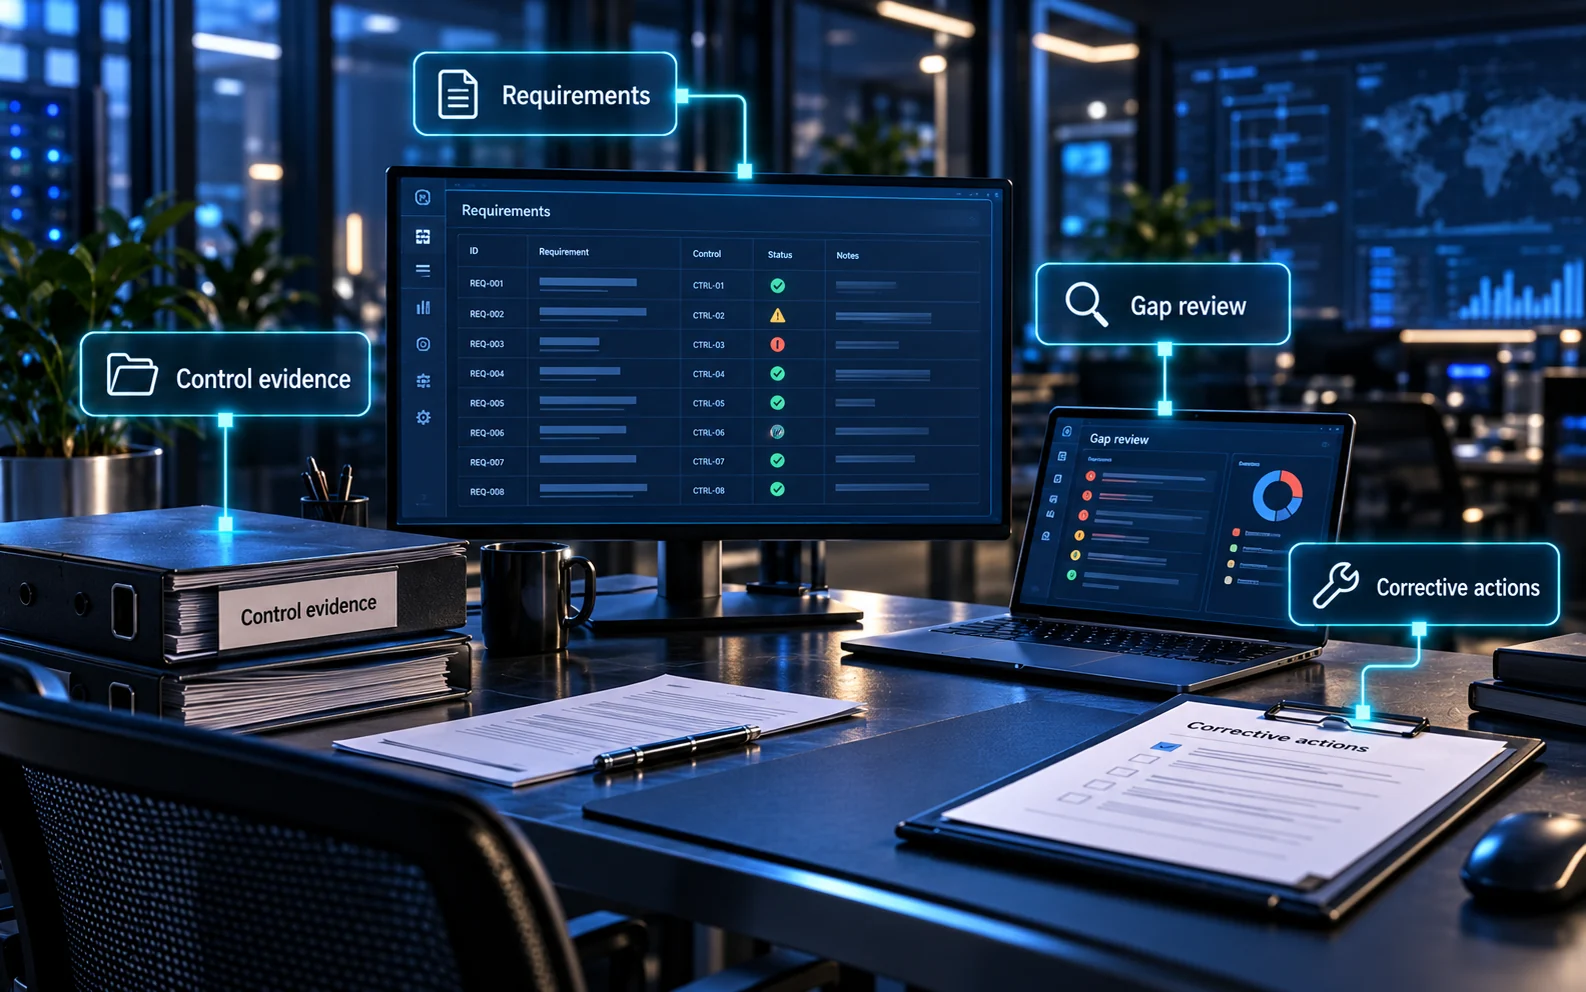
Use interviews to understand the process, documents to establish intended practice and samples to test what actually happens. For example, compare the access policy with recent joiner, mover and leaver records and the accounts still enabled.
Evidence confidence should be visible. A manager’s description, a single screenshot and a representative set of dated records provide different levels of assurance. Record unavailable evidence as a limitation rather than automatically treating the capability as either absent or effective.
| Evidence | What it can show |
|---|---|
| Policy or procedure | The intended rule and responsibility. |
| Configuration or system output | A setting or observed technical state at the time checked. |
| Operational records | Whether reviews, updates or response actions occurred over time. |
| Exercise or retest | Whether the organisation can perform the required action under realistic conditions. |
A detailed six-stage assessment and improvement process
1. Initiate and prepare
Agree which management decisions the assessment must support: allocating resources, understanding a newly acquired business, improving recovery or establishing a baseline. Identify the sponsor, service owners and assessment lead. Confirm the scope, framework version, evidence period and definition of each rating before interviews begin.
Request existing architecture, service and asset inventories, policies, supplier responsibilities, previous findings and incident/exercise records. A preparation call should identify unavailable evidence and arrange the right participants. Agree secure evidence transfer, progress reporting and how urgent findings will be escalated; do not wait for the final report to raise a material exposure.
2. Collect evidence across people, process and technology
Interview management, IT, security and operational staff, then compare their accounts with records and observed practice. Include suppliers when a capability depends on them. Follow a service or data flow across teams to reveal gaps that separate departmental questionnaires can conceal.
Use proportionate samples: a recent leaver, a privileged-access review, a restored service or a significant change. Record when the evidence was collected and what population it represents. Technical testing may strengthen the assessment, but penetration tests and intrusive scans need a separately agreed scope and authority; they are not automatically included in every maturity review.
3. Analyse gaps, dependencies and confidence
Compare observations with the chosen outcomes and rating definitions. Distinguish a missing control, inconsistent operation and insufficient evidence. A well-written procedure may coexist with ineffective implementation; conversely, a working practice may need formal ownership and records to become dependable.
Consider business consequence and dependencies alongside capability. A modest weakness affecting the identity provider for several critical services may deserve attention before a larger-looking gap in a low-impact system. Do not turn a maturity average into a quantitative probability of attack. Record limitations where access, sampling or contradictory evidence prevents a confident conclusion.
4. Draft, challenge and agree the report
Give owners an opportunity to correct factual errors and provide missing evidence. Keep a record of what changed and why. A disagreement about a rating should be resolved against the agreed method, not by negotiating a better-looking score. Unresolved uncertainty belongs in the report.
Present leadership with the material risks, dependencies, investment choices and residual exposure. Give implementers a more detailed evidence trail, required outcomes and verification criteria. Protect sensitive configuration and incident details in controlled appendices rather than spreading them through a broadly shared presentation.
5. Build a deliverable roadmap
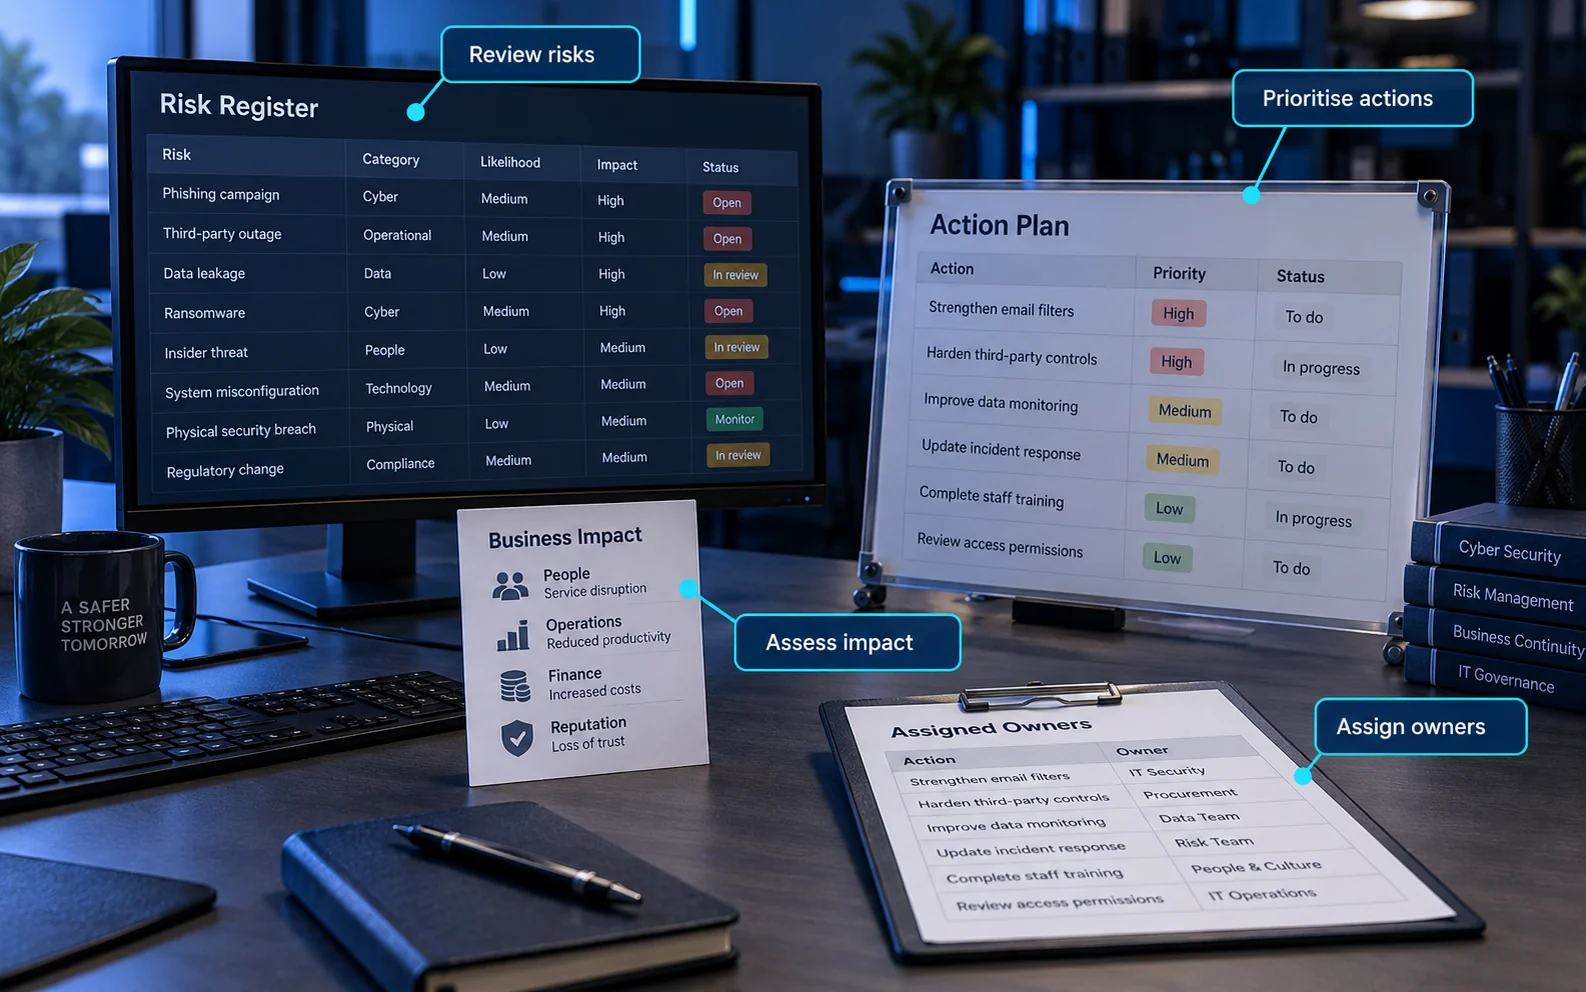
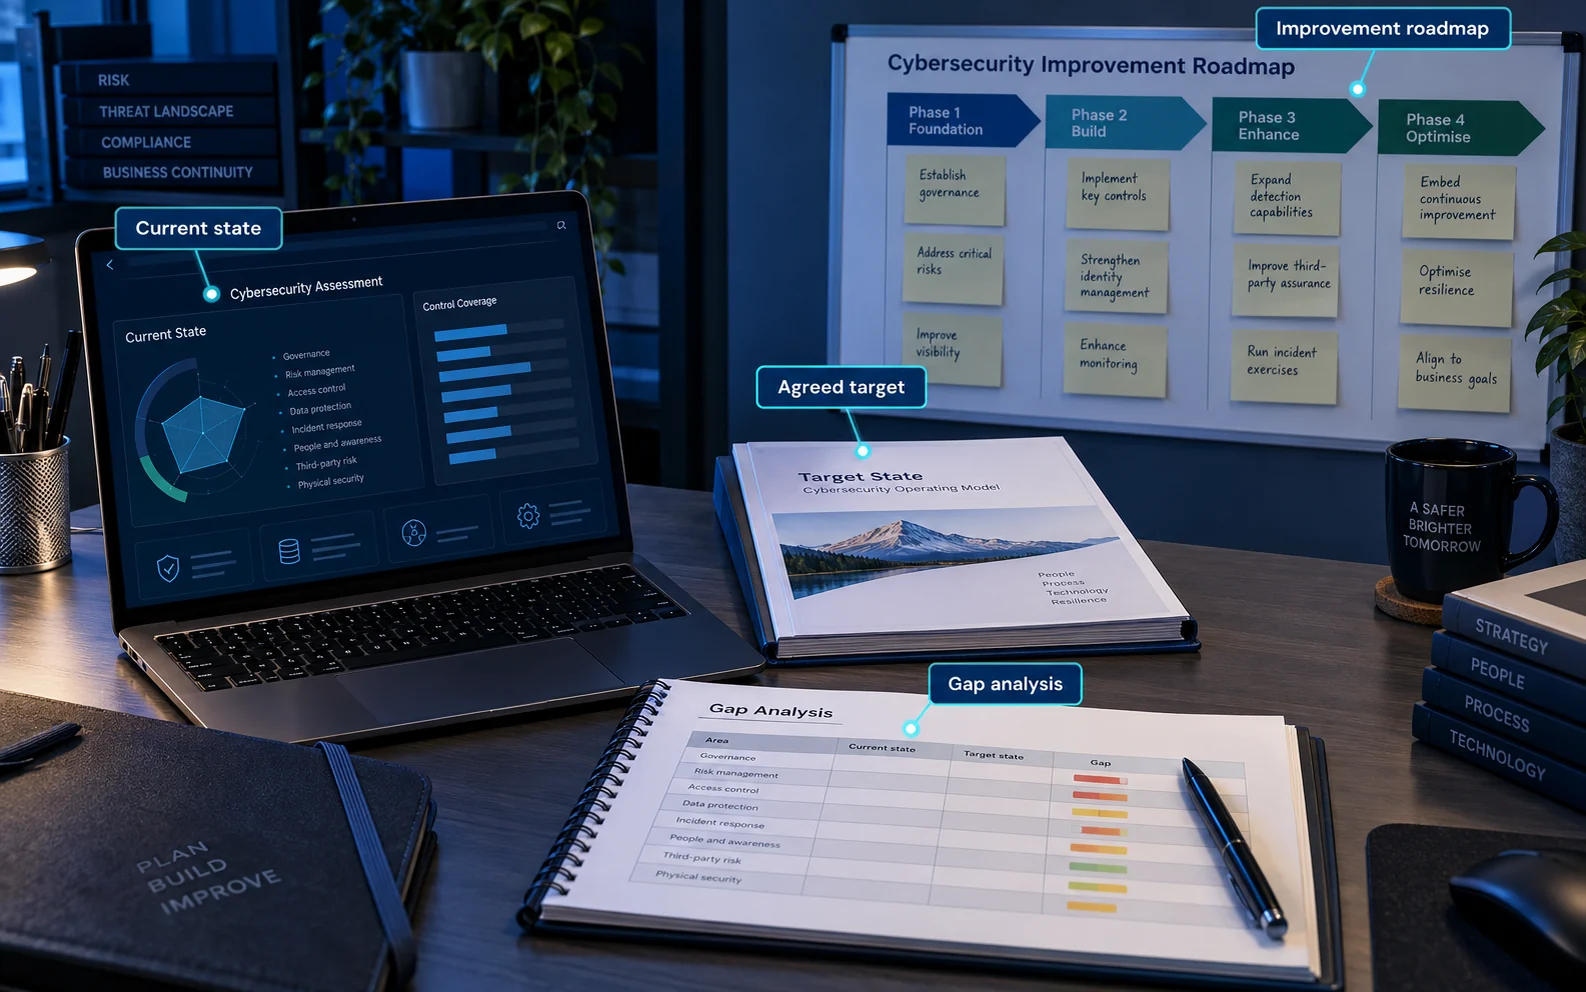
Translate each priority into an owned action, budget/resource need, dependency and completion test. Group foundational work where useful, such as service ownership, identity inventory and restore testing. Identify actions that can reduce immediate risk while larger redesigns are underway.
Illustrative planning horizons might be immediate containment, the next delivery cycle and a longer improvement programme. These are management choices, not standard deadlines. If a target cannot be delivered, record the decision, interim safeguards and residual risk rather than quietly lowering the requirement.
6. Validate, learn and reassess
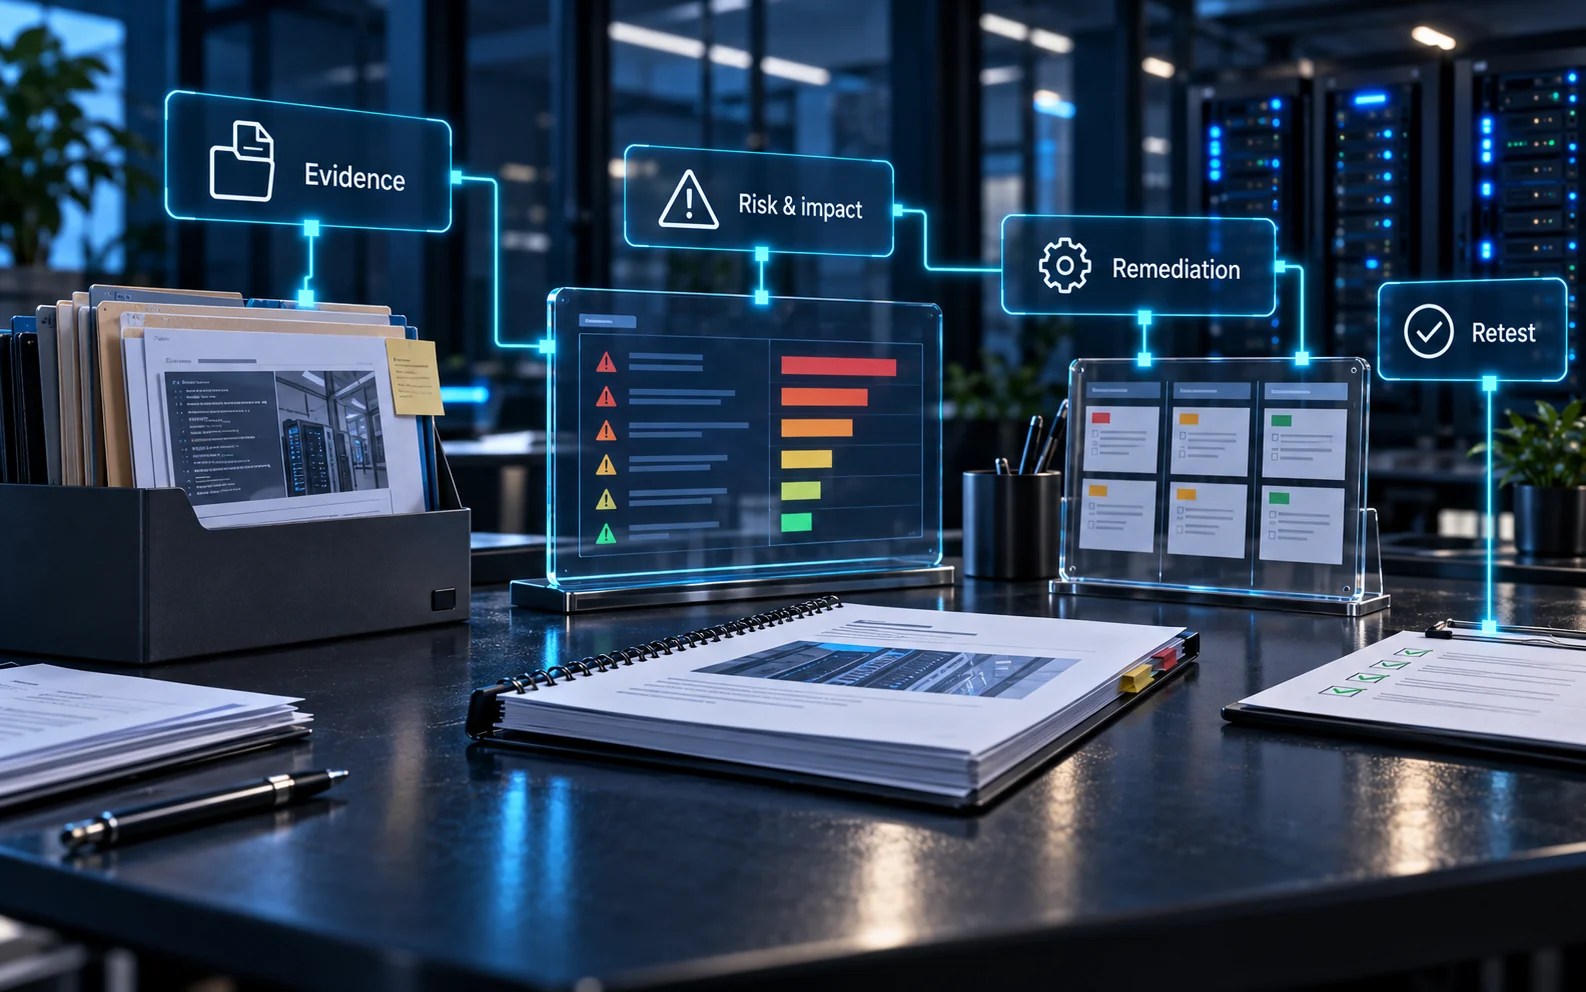
Check completed work against the original outcome. Ask for operating evidence or a practical demonstration, not only a closed ticket. Collect feedback from staff who use the new process and adjust training, responsibilities or tooling where it remains difficult to operate.
At reassessment, show whether scope, framework version, evidence quality or rating definitions changed. Report those differences before comparing scores. Record which improvements now work reliably and which still depend on a particular person, supplier or temporary workaround.
This delivery structure can be used with an appropriate chosen framework. NIST CSF resources support outcome-based discussions and current/target profiles; they do not make the illustrative six-stage process or local scoring rubric an official NIST maturity model.
An illustrative score with context
| Capability | Current observation | Illustrative rating | Confidence and target |
|---|---|---|---|
| Privileged access review | A policy exists, but only one system has recent review records. | 2 of 5: partly repeatable | Medium confidence. Target 3: named owners and recurring reviews across the agreed critical systems. |
| Backup recovery | Backups complete, but the business service has not been restored end to end. | 2 of 5: partly repeatable | High confidence in backup jobs; low confidence in service recovery. Target a witnessed restoration exercise. |
| Incident escalation | Contacts and authority were used successfully in a recent exercise. | 3 of 5: defined and demonstrated | Evidence relates to the tested scenario; test key supplier dependency next. |
These ratings are examples of a locally defined rubric, not official NIST levels or scores for ProCheckUp customers. Define every level and explain how evidence supports it. A target should reflect business need; the highest possible score is not automatically the best investment.
Prioritise a roadmap people can deliver
Rank actions by business impact, exposure, dependencies, effort and urgency. Deal with immediate material weaknesses while planning changes that take longer. Group related actions so several teams do not unknowingly solve the same problem.
| Action | Accountability | Completion evidence |
|---|---|---|
| Remove obsolete privileged access | Identity owner, with service-owner approval. | Access review and test showing revoked access no longer works. |
| Exercise recovery of a priority service | Service owner plus IT and key supplier. | Measured recovery, data-loss observation and recorded blockers. |
| Improve incident escalation | Response lead and management sponsor. | Exercise showing the correct person can make a timely containment decision. |
What a good report should contain
Expect a concise executive view, agreed scope, methods and limitations, evidence-supported findings, confidence statements and a prioritised action plan. The report should distinguish missing controls from insufficient evidence and explain consequential assumptions.
Leadership should be able to see which decisions need funding or risk acceptance. Technical and operational owners should be able to understand the required change and how completion will be checked.
Measure improvement and revisit assumptions
Use comparable scope and definitions when reassessing, or explain changes that make scores non-comparable. Track verified outcomes, overdue actions and unresolved dependencies, not just completed documents.
Revisit the target after a new service, acquisition, incident, regulatory change or major supplier change. A short targeted review may be more useful than repeating the entire assessment at every meeting.
Prepare the people and evidence for a useful handover
| Participant | Contribution | Question to resolve |
|---|---|---|
| Business sponsor | Service priorities, resources and risk decisions. | Which failure matters most, and who can approve corrective work? |
| Service and operational owners | Dependencies, workarounds and the real effect of disruption. | Does the proposed control work in normal operations and during an outage? |
| IT/security teams | Configurations, events, changes and technical constraints. | Can the intended practice be demonstrated across the agreed scope? |
| HR, procurement and other support teams | Joiner/leaver, supplier and approval processes. | Where do responsibilities pass between teams? |
| Assessor | Method, evidence trail, limitations and recommendations. | Which conclusions are supported, uncertain or outside the review? |
For example, a recovery gap may need the business to set acceptable downtime, IT to establish restore capacity and a supplier to provide an export or recovery interface. “Buy better backup” is not a complete action. A useful handover identifies each dependency and the end-to-end test that will show the service can be used again.
Common questions
Is this a certification?
Not by itself. It is an assessment against an agreed method. Any separate certification has its own scope, requirements and assessment process.
How should a small organisation start?
Select its most important service, map dependencies and examine a small set of high-impact practices such as access, updates, backup recovery and incident escalation. Expand from the evidence.
How long will it take?
It depends on scope, evidence availability, interviews and required technical validation. Agree deliverables and access before estimating effort.
Related guidance
Technical testing · A practical SME security policy · Cyber Essentials baseline controls
Need Help?
If you have any questions about cyber security or would like a free consultation, don't hesitate to give us a call!
For More Information Please Contact Us
ACCREDITATIONS