Cyber Maturity Assessment
A cyber maturity assessment shows how consistently an organisation manages security and where improvement will have the most value.
Why Cyber Maturity Assessment?
In today's interconnected digital ecosystem, even a minor vulnerability can result in significant damages. From reputational loss to financial implications, the stakes have never been higher. A CMA isn’t just about finding vulnerabilities; it's about understanding, planning, and setting a road-map for continual cyber security improvement.
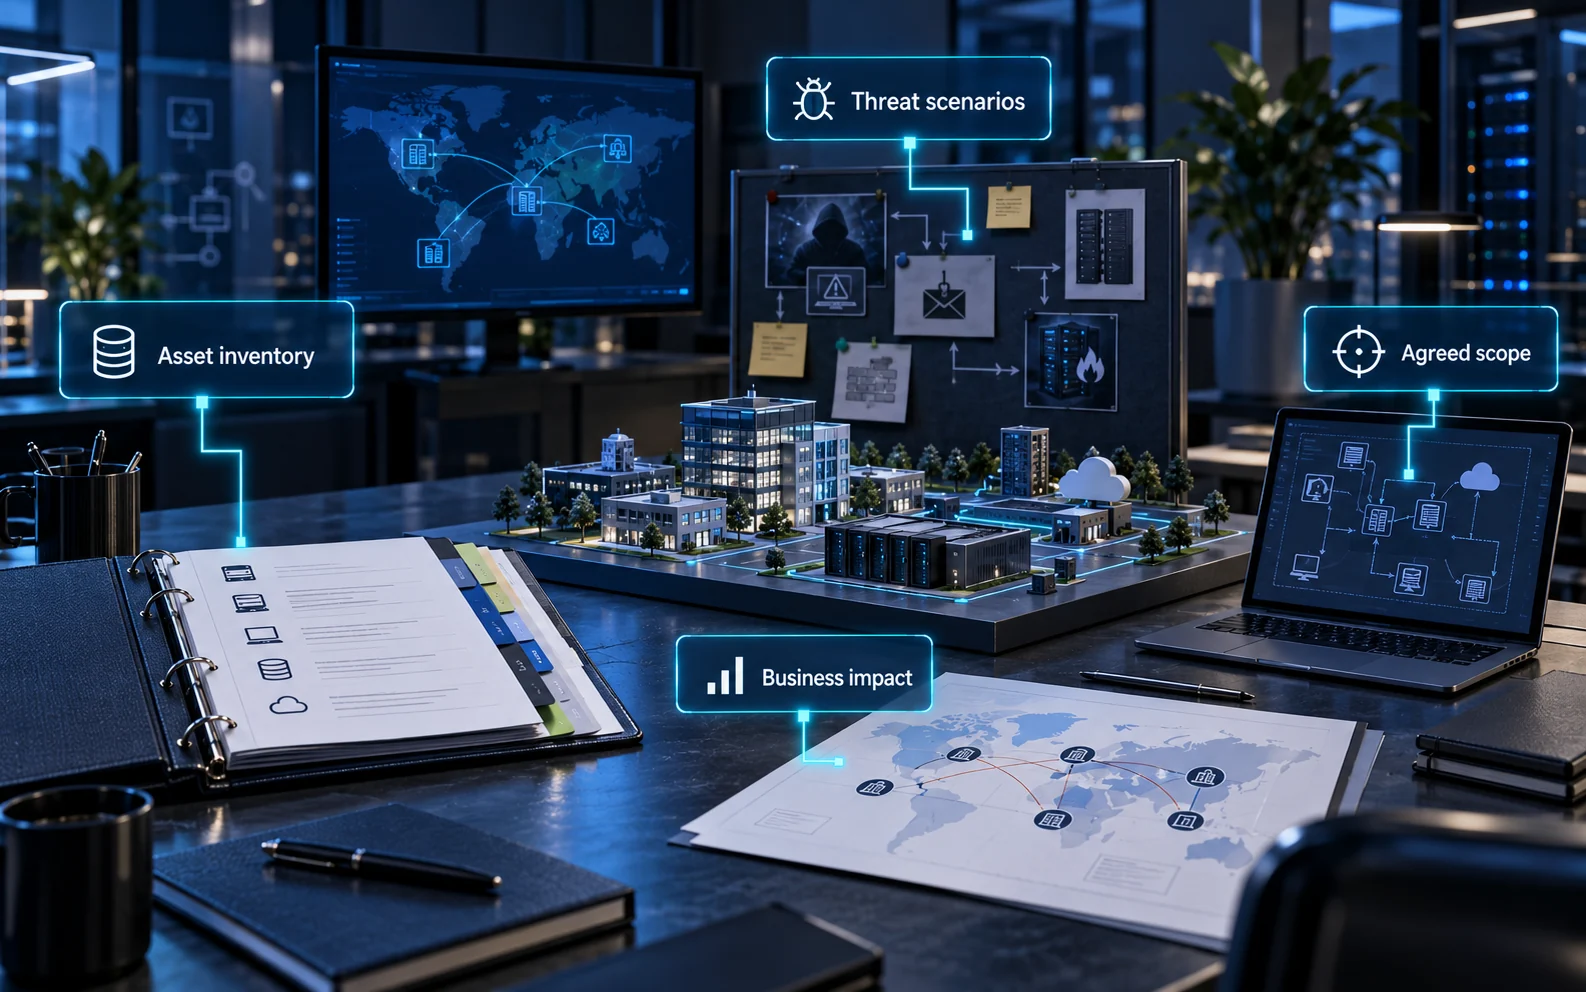
Components Of A Cyber Maturity Assessment:
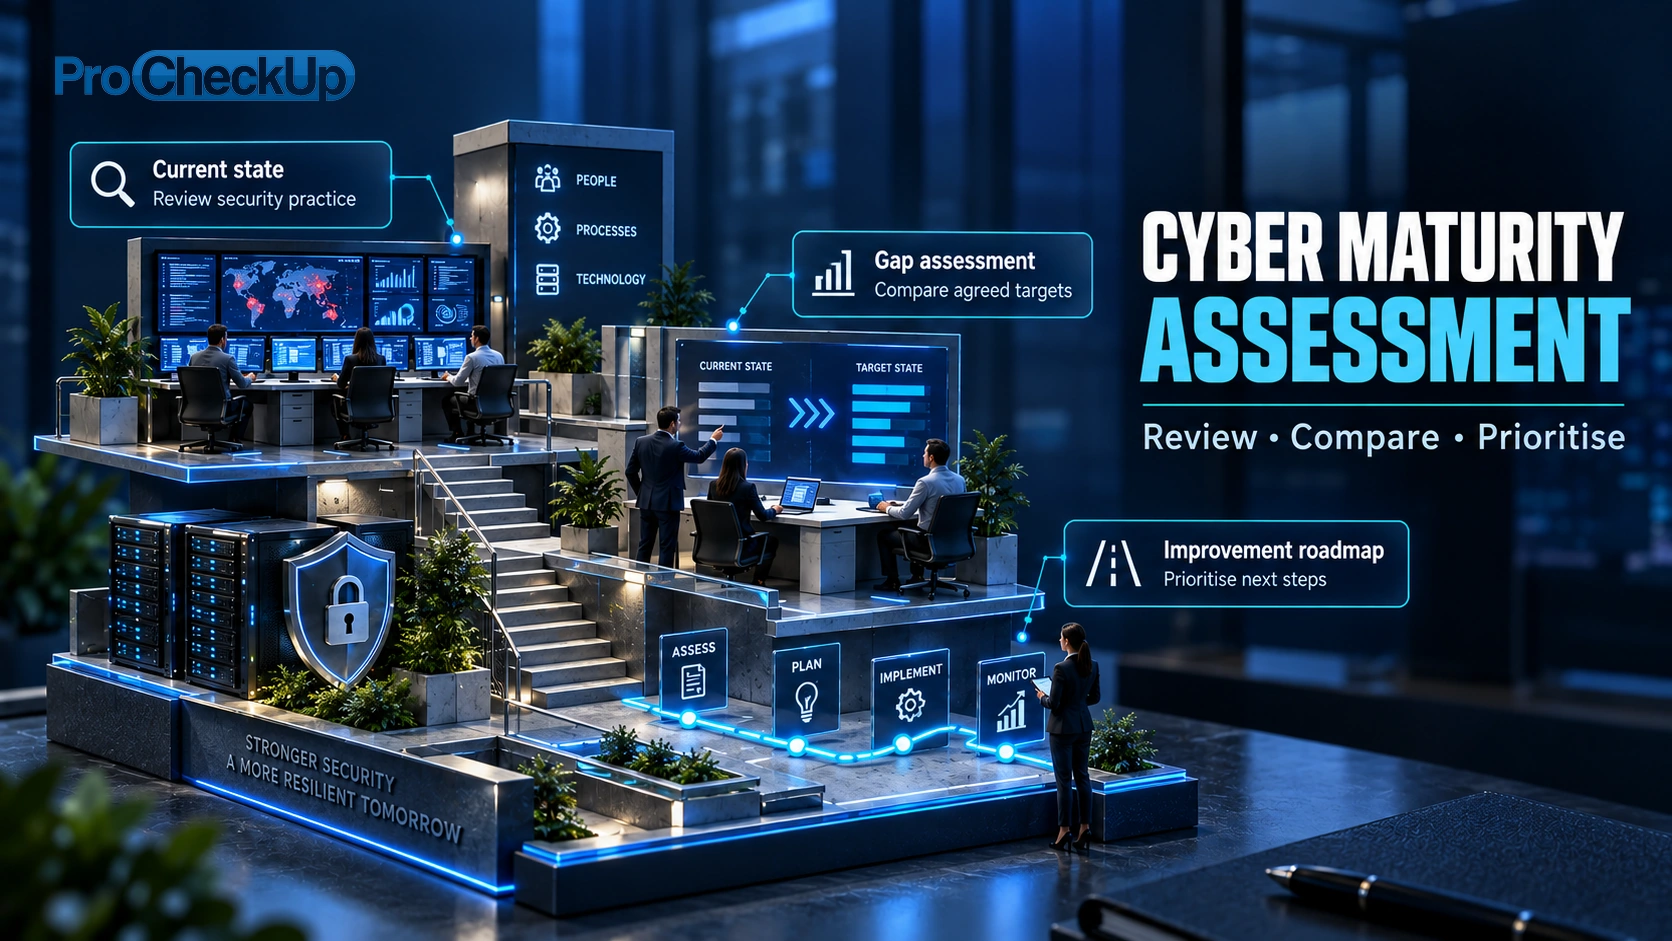
Current State Analysis: Evaluate your existing cyber security controls, technologies, and processes.
Risk Assessment: Understand potential threats specific to your industry and business model.
Benchmarking: Compare your practices against industry standards and best practices.
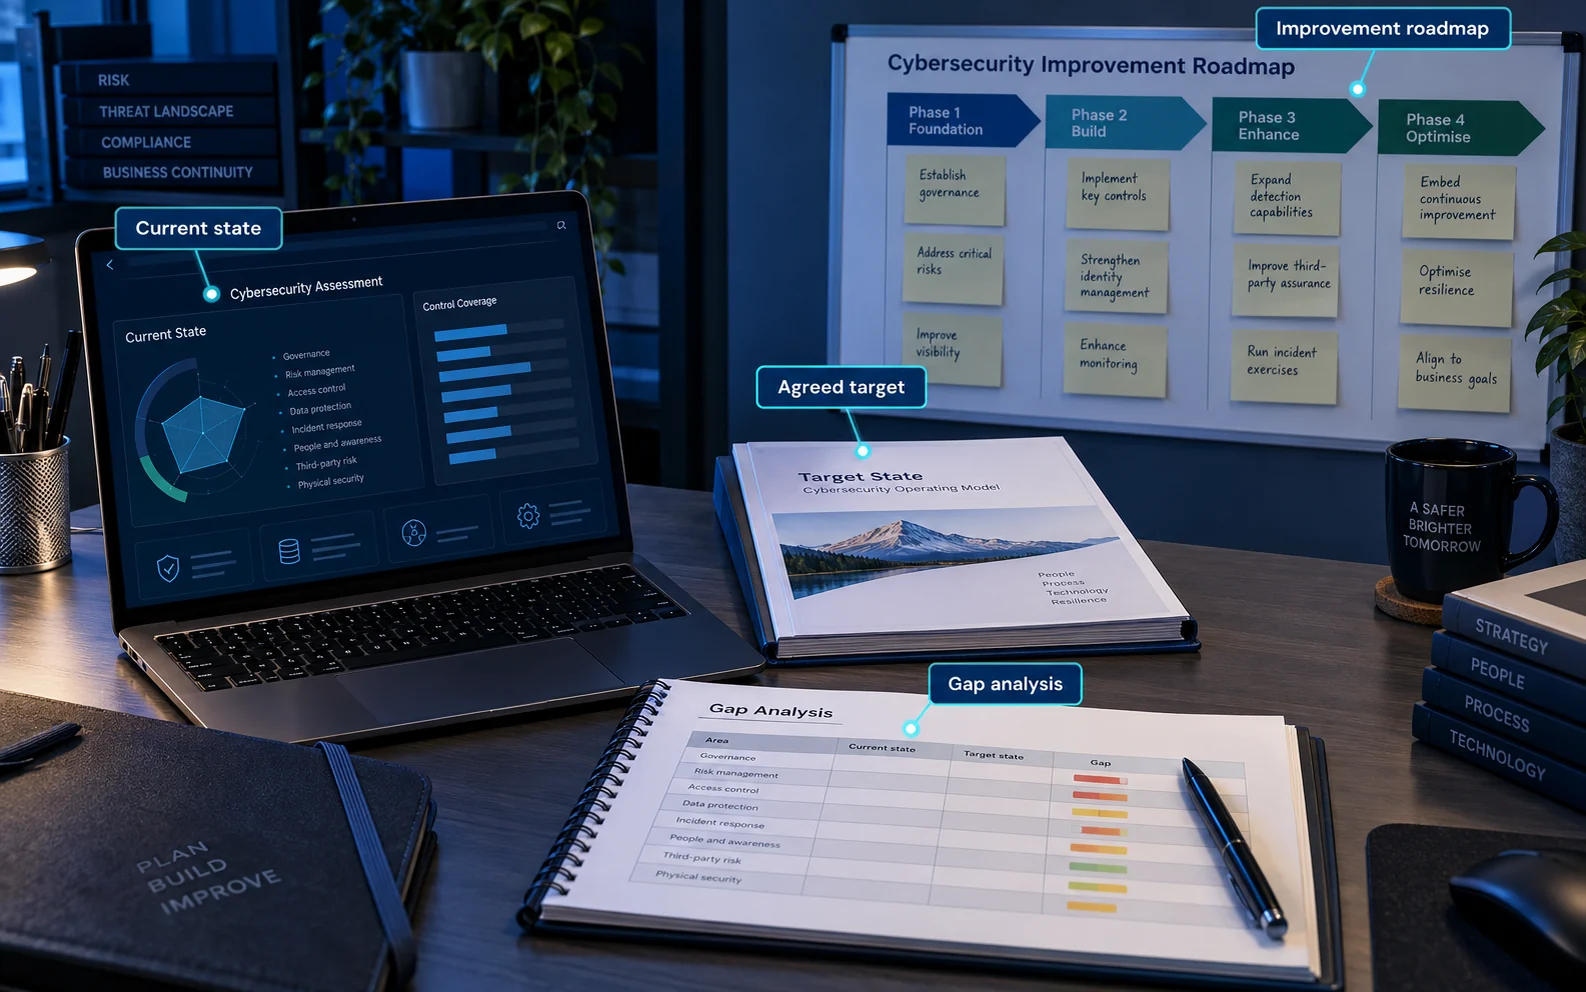
Gap Analysis: Identify areas where your cyber security practices fall short.
Roadmap Creation: Develop a structured plan to advance your cyber security maturity over time.
- Current State Analysis
Evaluate your existing cybersecurity controls, technologies, and processes.
- Risk Assessment
Understand potential threats specific to your industry and business model.
- Benchmarking
Compare your practices against industry standards and best practices.
- Gap Analysis
Identify areas where your cybersecurity practices fall short.
- Roadmap Creation
Develop a structured plan to advance your cybersecurity maturity over time.
Framework and scoring approach
Governance, risk ownership and security responsibilities
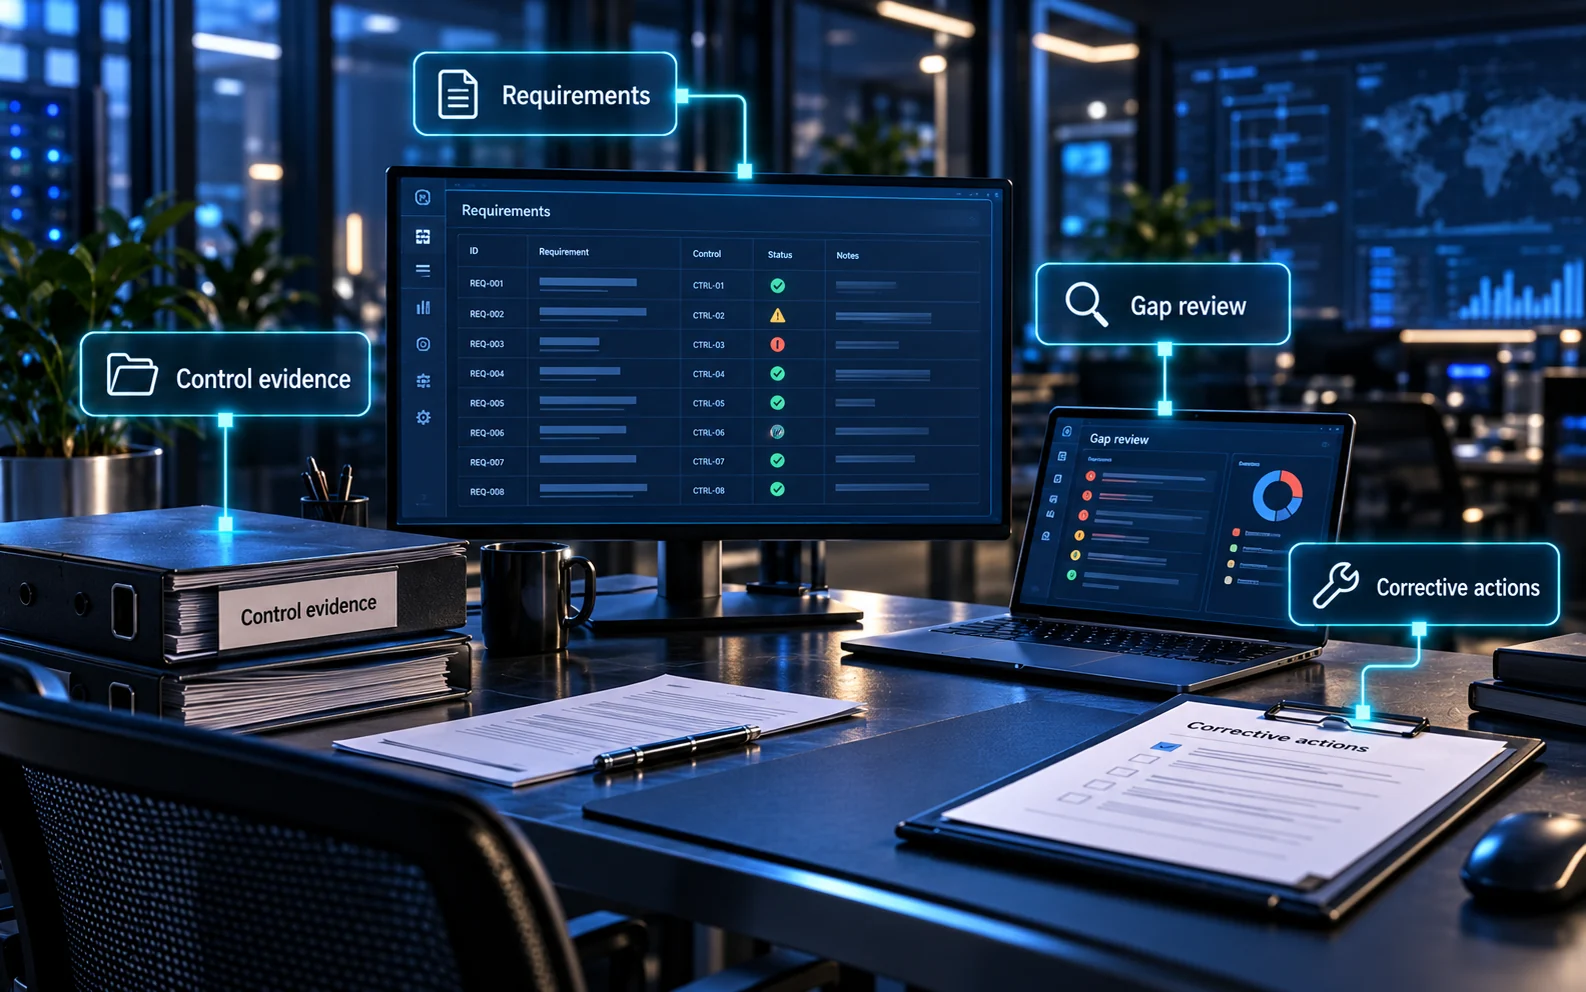
Evidence of preventive, detective and response capabilities
Gaps between current practice and the agreed target state
Benefits:
Informed Decision Making: Understand where to invest your cyber security budget for maximum impact.
Regulatory Compliance: Ensure your cyber security practices meet and exceed industry regulations.
Stakeholder Confidence: Showcase your commitment to cyber security, earning trust from clients, partners, and stakeholders.
Competitive Advantage: Stay ahead of competitors by ensuring that your business is protected against the latest threats.
ProCheckUp's Cyber Maturity Assessment (CMA) offers a comprehensive evaluation of your organisation's cyber security practices, policies, and procedures, bench-marked against globally recognized standards.
How Our CMA Process Works:
Initiation: Understand your business objectives, existing cyber security infrastructure, and any specific concerns.
Data Collection: Use interviews, surveys, and advanced scanning tools to gather relevant data.
Analysis: Evaluate the collected data against global standards and best practices.
Report Generation: Produce a detailed assessment report highlighting current maturity level, gaps, and recommendations.
Feedback Session: Discuss the findings and collaborate on creating a road-map for improvement.
- Initiation
Understand your business objectives, existing cybersecurity infrastructure, and any specific concerns.
- Data Collection
Use interviews, surveys, and advanced scanning tools to gather relevant data.
- Analysis
Evaluate the collected data against global standards and best practices.
- Report Generation
Produce a detailed assessment report highlighting current maturity level, gaps, and recommendations.
- Feedback Session
Discuss the findings and collaborate on creating a roadmap for improvement.
Who Needs a Cyber Maturity Assessment?
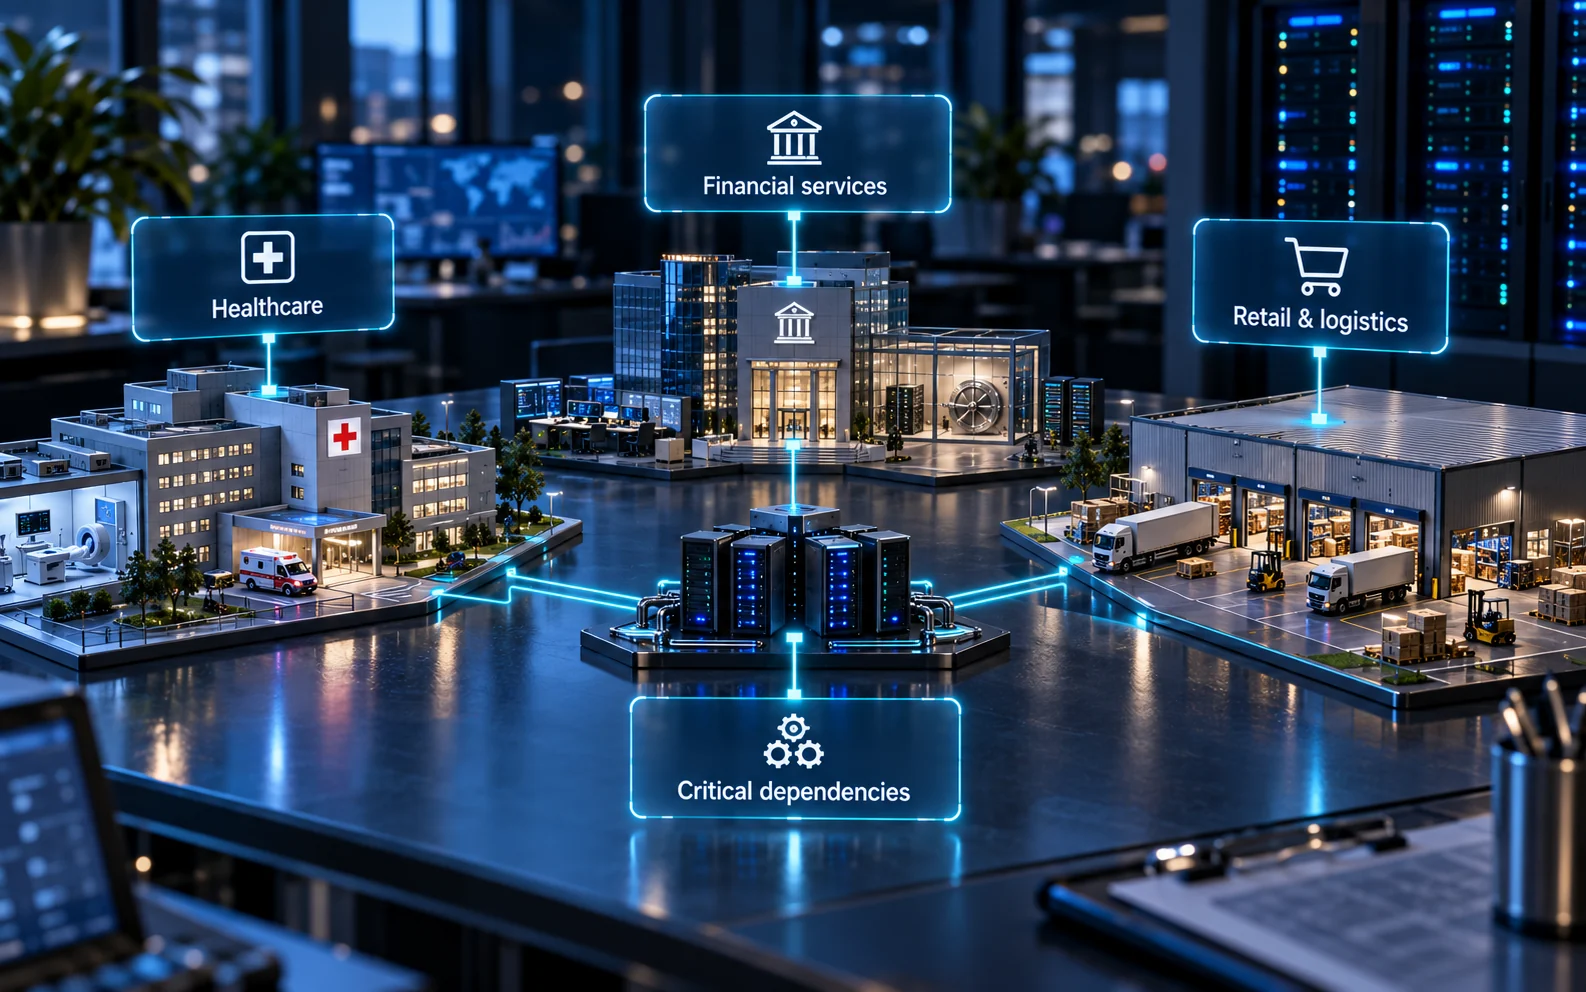
Whether you're a budding startup, a growing SME, or a well-established enterprise, understanding the maturity of your cyber security efforts is vital. This assessment is particularly beneficial for:
Industries with strict regulatory compliance: Financial services, healthcare, energy, and others with strict data protection laws.
Businesses undergoing digital transformation: As you integrate more digital tools and platforms, understanding security maturity becomes even more vital.
Organisations with a high dependency on digital data: E-commerce platforms, online service providers, and other digital-first businesses.
What Sets Our CMA Apart?
Expertise: Our team comprises professionals with years of experience and certifications in the cyber security domain.
Tailored Approach: We don't believe in a 'one-size-fits-all' strategy. Our assessments are tailored to your industry and business needs.
Actionable Insights: Beyond pointing out gaps, we offer actionable solutions to enhance your cyber security posture.
Continuous Collaboration: Our relationship doesn't end with the assessment. We're here to support you in your journey towards improved cyber security maturity.
Frequently Asked Questions (FAQs):
Q: How long does the assessment take?
A: The duration can vary based on the size of your organisation and the complexity of your digital infrastructure. Typically, it ranges from a few days to a few weeks.
Q: Will my day-to-day operations be disrupted?
A: We strive to ensure minimal disruption. Most data gathering can be done without impacting regular operations.
Q: How often should I undertake a CMA?
A: The digital threat landscape is ever-evolving. We recommend a CMA at least once a year or whenever there's a significant change in your digital operations.
Preparing for the engagement
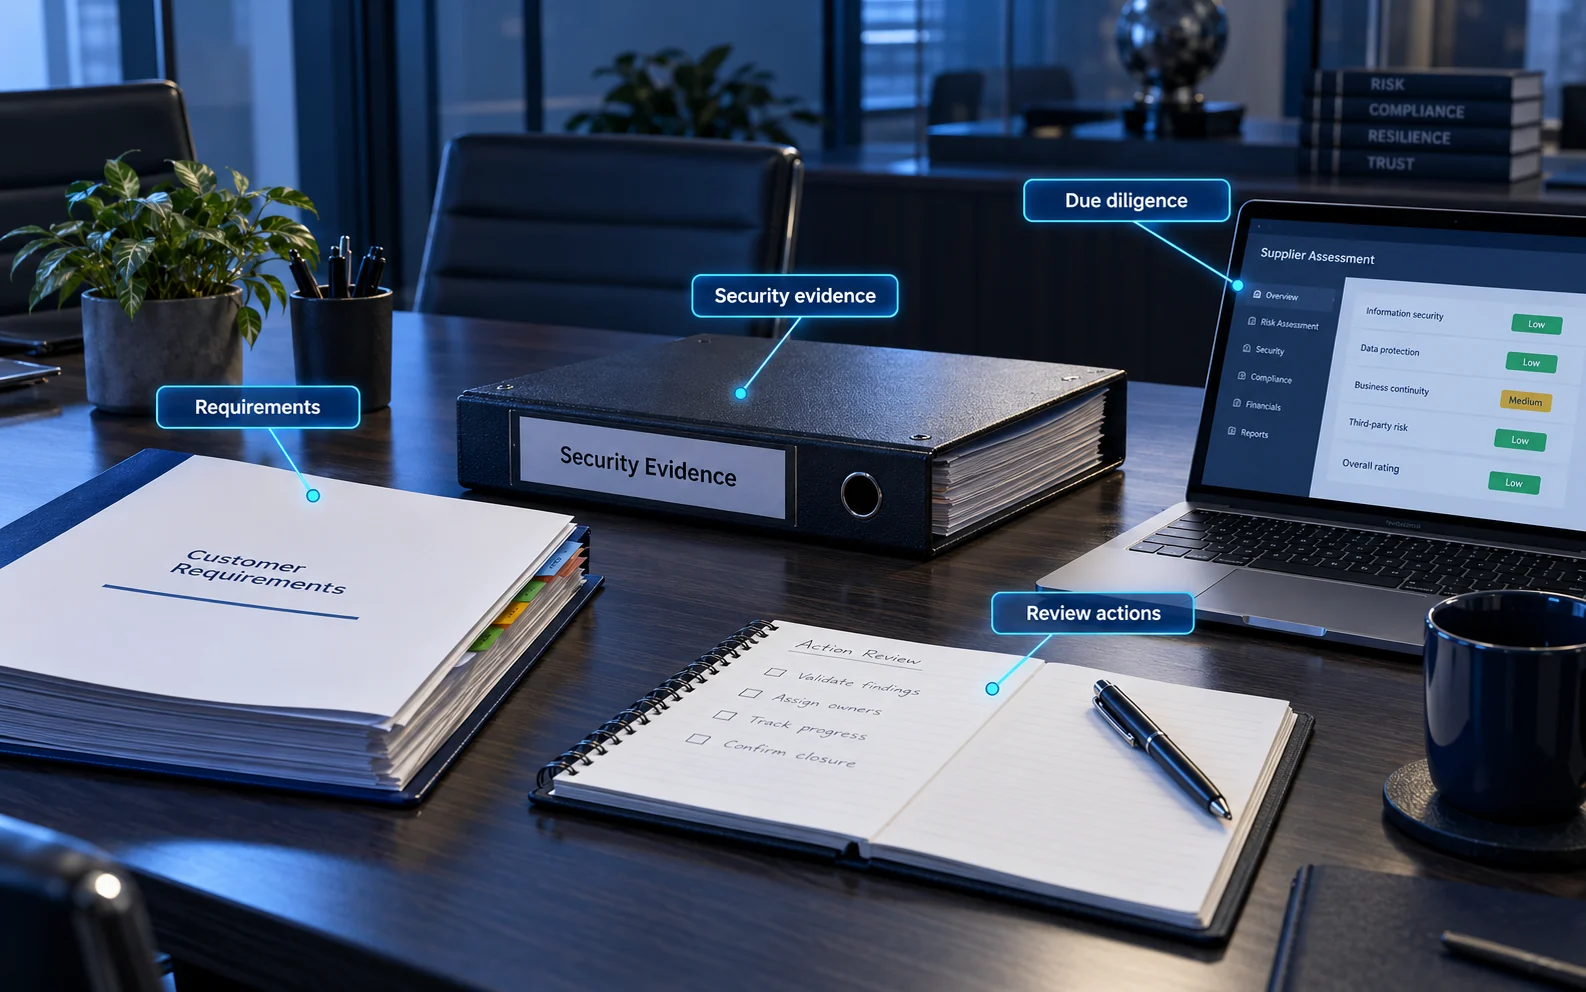
Agree the framework, scoring criteria and business services in scope. Interviews, existing assessments, policies and operational records help distinguish documented intentions from working controls.
Outcomes and next steps
A useful assessment explains the evidence behind each conclusion and sets out priorities, owners and dependencies. The resulting roadmap supports investment decisions and future reassessment.
Related services
Discuss your requirements
Contact ProCheckUp with the environment, objectives and timing you have in mind. We can discuss the appropriate scope and next steps.
Need Help?
If you have any questions about cyber security or would like a free consultation, don't hesitate to give us a call!
For More Information Please Contact Us
ACCREDITATIONS