Open-source intelligence (OSINT) assessments
Understand what publicly available information reveals about your organisation and which exposures need attention. ProCheckUp’s open-source intelligence (OSINT) assessments investigate information linked to your organisation, domains, brands and other agreed targets.
We assess the evidence behind each observation to help your team distinguish credible risks from uncertain associations, prioritise remediation and decide where further investigation is needed.
What an OSINT assessment can reveal
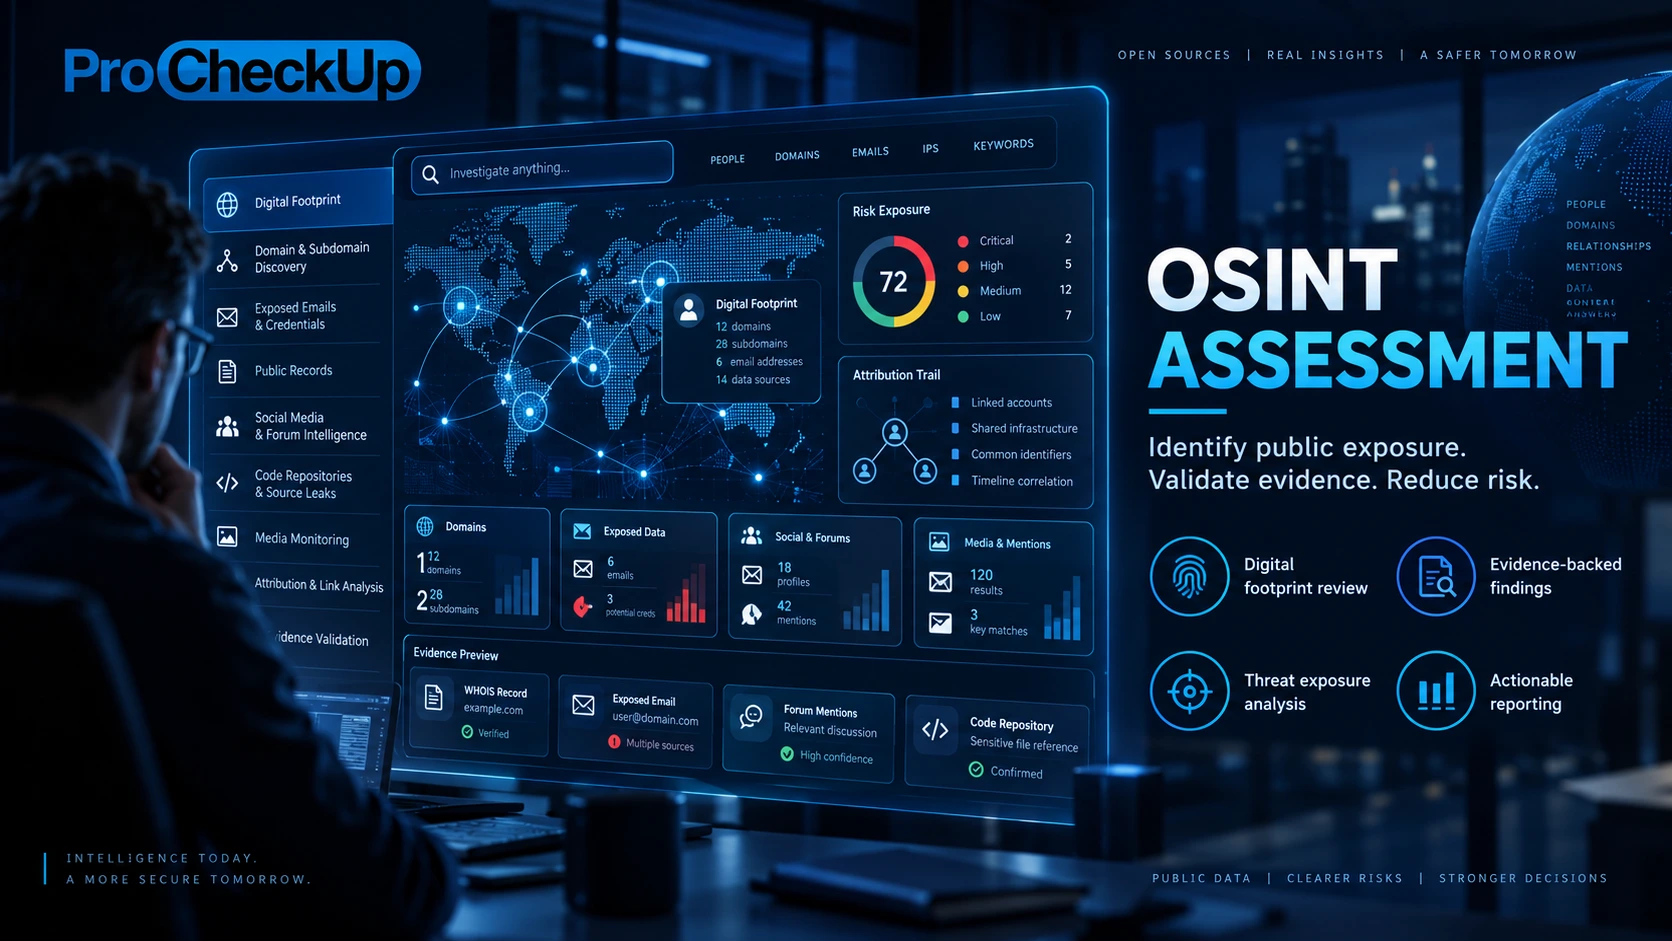
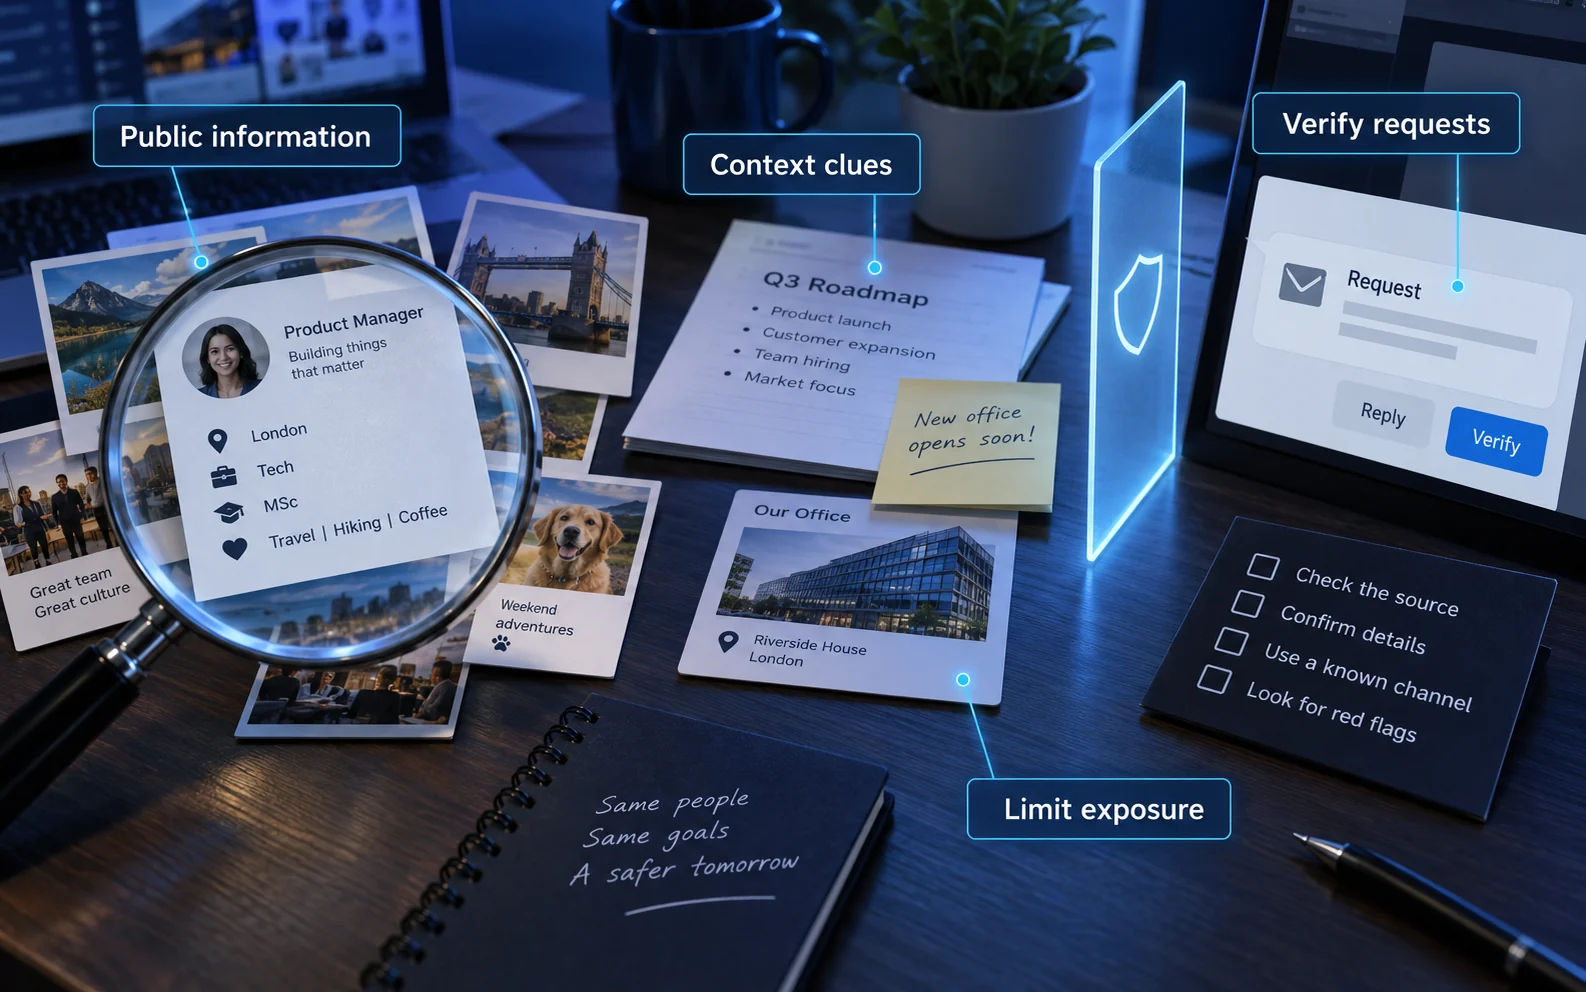
Information published across different sources can reveal more when considered together. Depending on the agreed scope, an assessment can examine:
Public exposure: references to your organisation, brands, domains and services that help establish its online presence.
Sensitive material: credentials, configuration details or business information exposed in public repositories and documents.
Relationships and context: links between public records, websites and other sources, with the strength of each association assessed.
Security implications: how the information could support impersonation, targeted attacks or unauthorised access, and what evidence is needed to assess that risk.
When to use an OSINT assessment
Start with the decision you need to make. Common assessment questions include:
Reviewing your public footprint: what can an external party discover about the organisation, and which disclosures deserve attention?
Investigating a suspected exposure: where does sensitive information appear, how does it relate to your systems, and what needs urgent action?
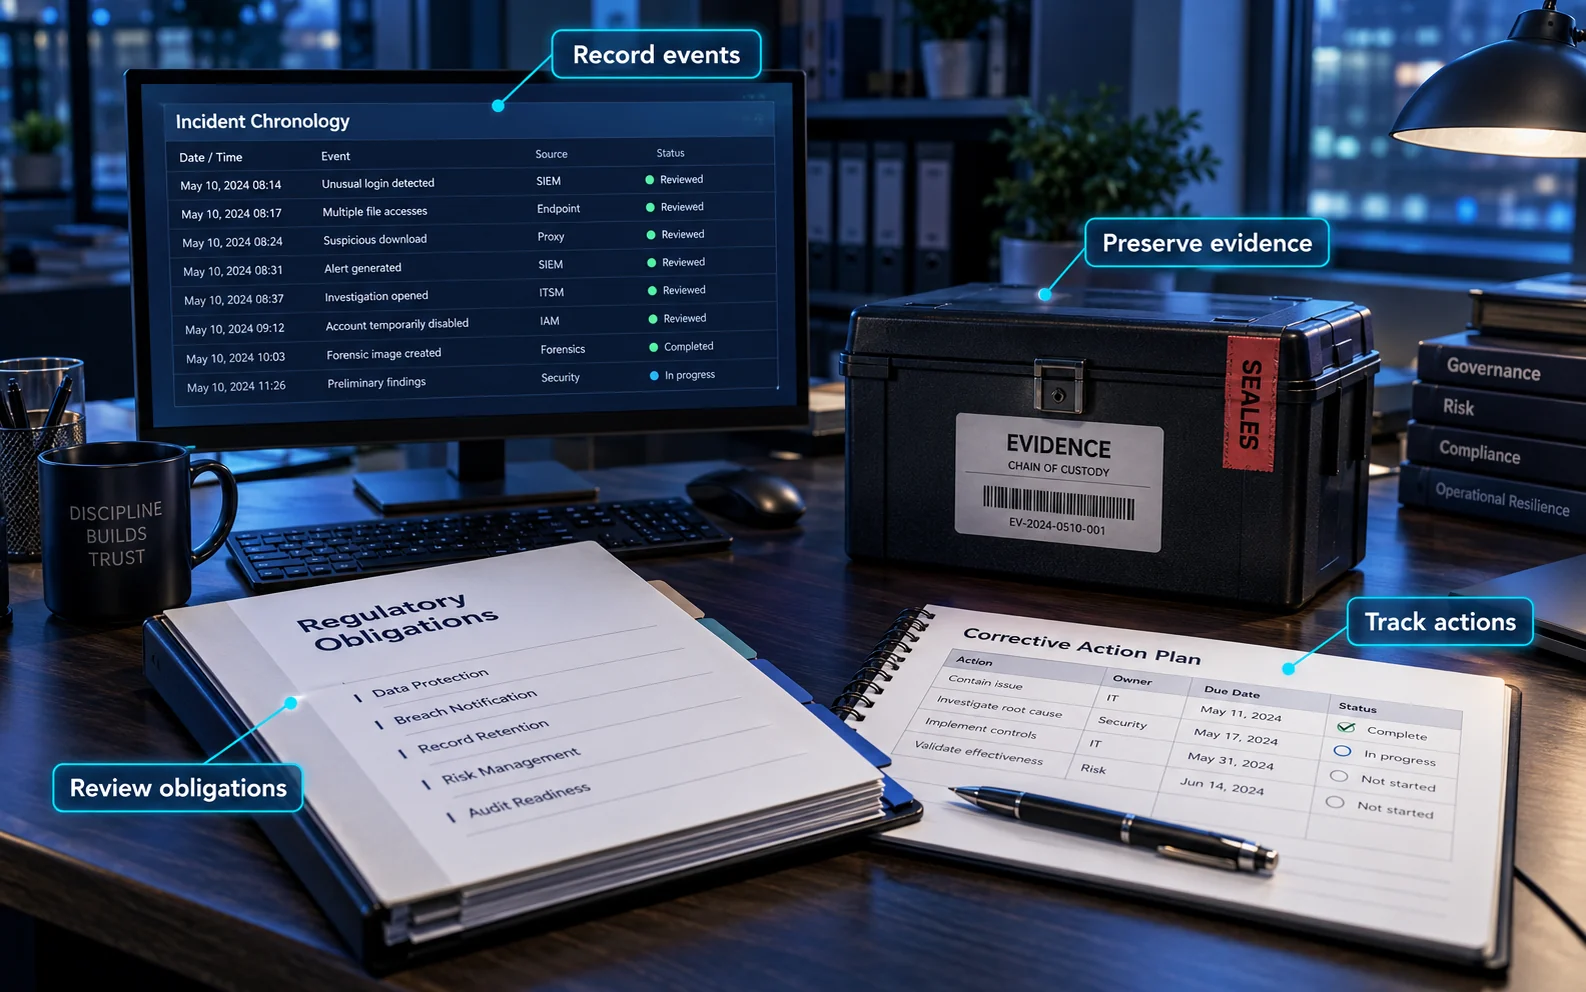
Supporting an incident investigation: which public observations add useful context, and which questions require internal logs or forensic evidence?
A clear objective keeps the research focused on information that supports a practical security decision.
Sources and evidence quality
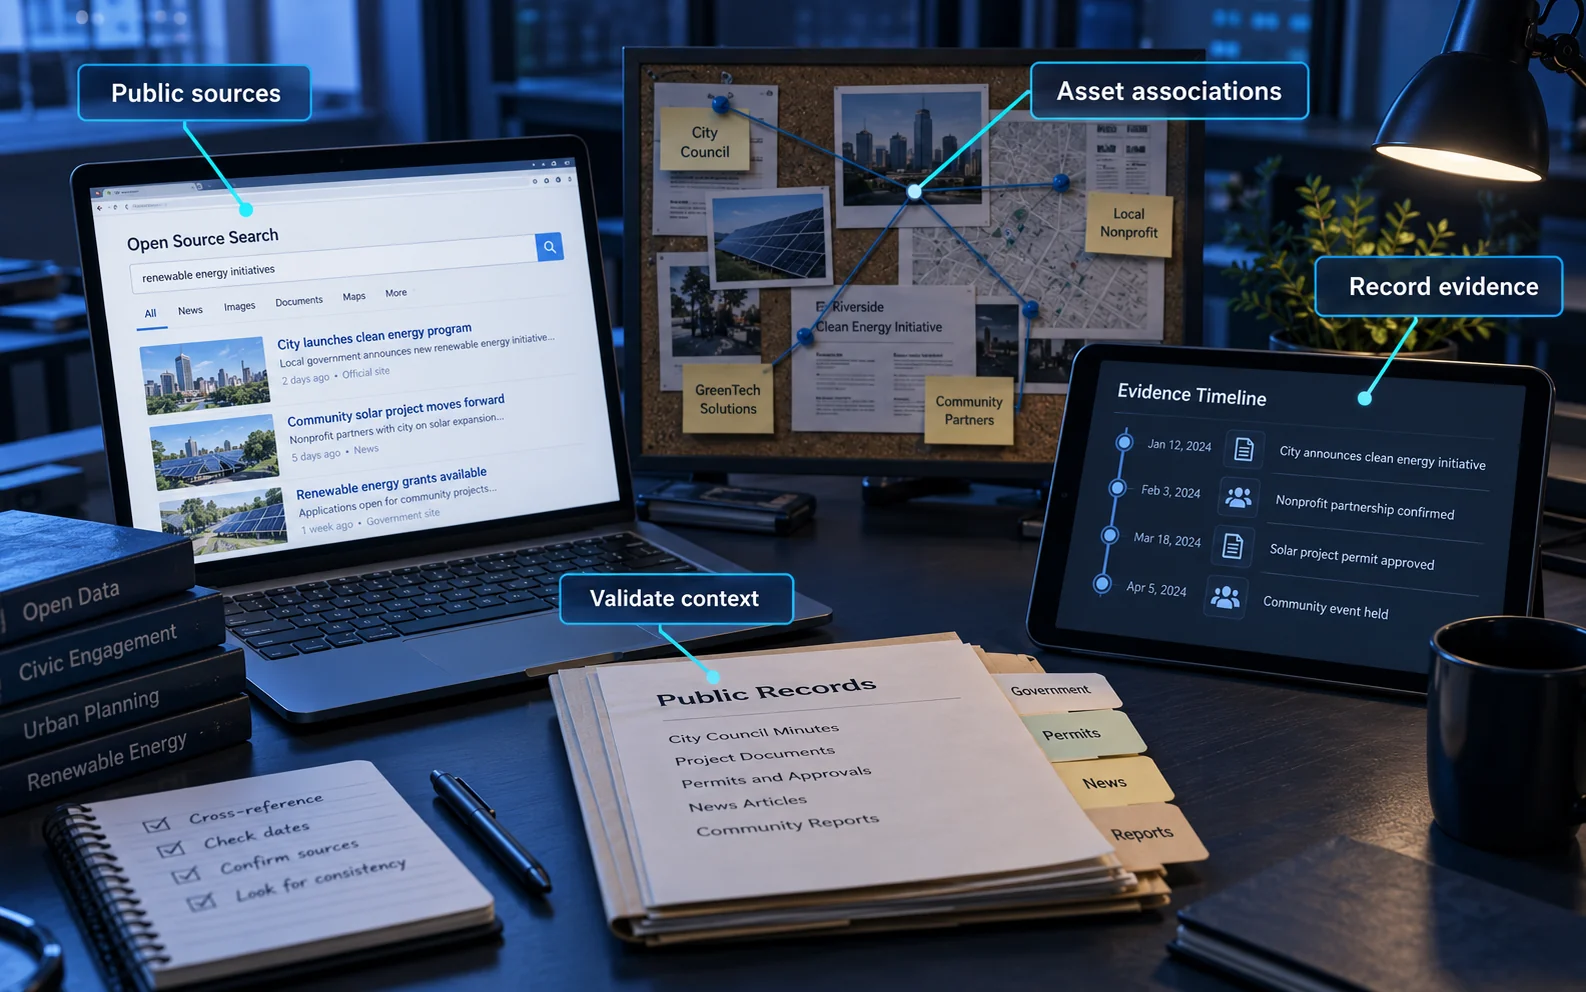
Relevant sources may include public code repositories, developer forums, company filings, public records, news reports, websites and social platforms. Each observation needs context: where it was found, when it was published or observed, and how confidently it can be linked to the agreed target.
Search and analysis tools can help locate information and identify possible relationships. Results still require review: a matching name, linked entity or indexed service does not by itself establish ownership or a vulnerability.
Passive research and authorised validation
Passive research examines information already available from public sources. Discovering a credential or a reference to a system does not establish that access is possible or that a compromise has occurred.
Testing access is a separate activity. Authentication attempts and other active checks require an agreed target, explicit authorisation and defined limits. Any validation must stay within those boundaries.
Where access has not been tested, or a check is inconclusive, the finding remains unverified. An unsuccessful check is not sufficient evidence that an exposed secret is safe.
Case study: from repository exposure to action
In our GitHub credential leak investigation, ProCheckUp reviewed approximately 800 repositories and identified more than 2,300 instances of potentially sensitive material. The engagement combined repository analysis, OSINT and a separately authorised validation phase.
Selected credentials were classified as active, inactive or unverified. This helped the customer prioritise remediation. Validation stopped once authentication was confirmed; customer data was not accessed and resources were not changed.
Example finding: an exposed email-service credential
The same engagement identified an active SendGrid key with extensive administrative permissions.
Evidence: repository discovery and authorised validation confirmed the credential’s status.
Potential impact: misuse of the associated email service. The finding did not establish that an attacker had used the key.
Response: revoke or rotate the key, review service logs, remove the exposed secret and verify that the old credential no longer works.
Read the full case study for the testing boundaries and remediation approach.
Understanding the limits of OSINT
Accuracy: public information can be outdated, incorrect or associated with another organisation. Findings need to distinguish confirmed facts from uncertain links.
Coverage: reviewing agreed sources cannot prove that no other exposure exists.
Timing: results reflect the evidence available during the assessment. Public content and access permissions can change.
Handling: publicly accessible information may still be personal or sensitive. Its collection, use, sharing and retention need agreed boundaries.
OSINT can support an investigation, but establishing who accessed a system or used a credential usually requires additional evidence.
Reporting and remediation priorities
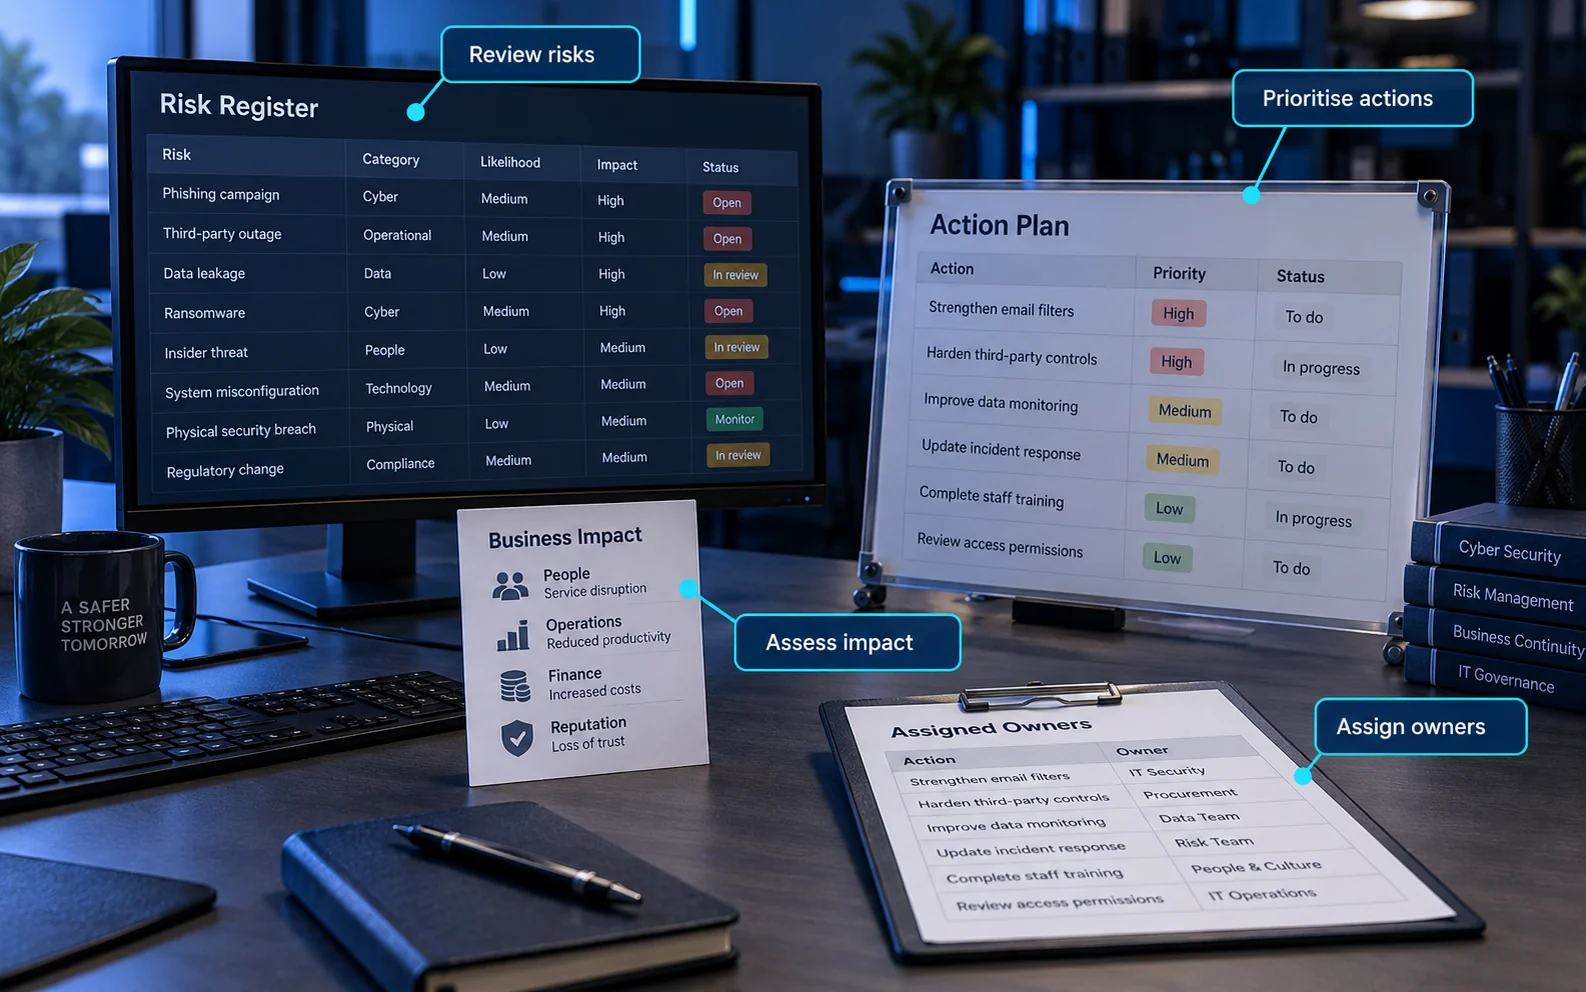
Useful findings connect evidence to action. They should explain the source, the confidence in the observation, its relevance to your organisation and the recommended next step.
Use those findings to assign owners, prioritise remediation and identify checks that need further evidence or authorisation. Depending on the exposure, actions may include removing sensitive content, rotating credentials, reviewing access permissions or investigating service activity.
Planning your OSINT assessment
To scope the work, bring:
Your objectives, priority concerns and the decisions the findings need to support.
The organisations, brands, domains, repositories and other targets you are authorised to include, together with exclusions and third-party assets.
Relevant background, known exposures and any timing or information-handling requirements.
Any concerns about evidence quality, attribution or potential exposure that the assessment should resolve.
A contact who can confirm ownership, resolve scope questions and coordinate action on findings.
Share sensitive evidence through an agreed channel. Keep passwords, access tokens and confidential material out of the initial contact form.
Delivery, escalation and follow-up
Before work starts, agree the assessment priorities, schedule, report format and recipients. The number of targets, sources and attribution questions will influence the effort required.
Nominate an escalation contact for urgent findings, such as an apparently active exposed credential. Agree secure delivery, evidence retention and any follow-up validation or remediation checks as part of the scope.
Related security services
GitHub credential discovery and validation for repository exposure and expressly authorised credential checks.
Incident response and forensics for investigation using internal systems, logs and other evidence.
Security assessment services for wider technical and organisational security questions.
Discuss your OSINT assessment
Contact ProCheckUp with your objectives, the types of target you want to assess and your preferred timeframe. We can discuss the scope, priorities and next steps for your organisation.
Need Help?
If you have any questions about cyber security or would like a free consultation, don't hesitate to give us a call!
For More Information Please Contact Us
ACCREDITATIONS