
Local government security assessments need to reflect the council services, information and public access arrangements they protect. ProCheckUp reviews agreed technical and physical controls to help teams identify practical improvements.
Local Government Sector
Quick Introduction:
In the ever-evolving digital landscape, local government entities in the UK face a myriad of cyber security challenges. Tasked with the stewardship of sensitive citizen data and critical infrastructure systems, these bodies are prime targets for cyber threats. Balancing accessibility with security, local governments must navigate a complex web of regulations and threats while striving to provide seamless public services.
The cyber security regulatory environment in the UK is robust, providing a framework for local governments to secure their digital assets and data. Here are the top cyber security regulations and standards that apply to this sector:
Local governments may face challenges such as budget constraints, limited cyber security expertise, or the complexity of their IT infrastructure. Overcoming these requires strategic investment in cyber security and continuous training of IT personnel.
Cyber security Regulations
NCSC Check Penetration Testing:
Local governments must demonstrate a proactive stance against cyber threats, and one of the key methodologies is through NCSC Check Penetration Testing. This rigorous testing process involves simulating cyber-attacks to identify vulnerabilities within IT systems and networks.
Scope and Importance:
NCSC Check tests are designed to identify exploitable vulnerabilities in internet-facing systems and internal networks. For local governments, the importance of such assessments cannot be overstated, as they often hold data pertaining to national security and public welfare.
Compliance Steps:
- Engage: with an NCSC-approved Check service provider's like ProCheckUp.
- Define the scope of the penetration test:, including systems, applications, and infrastructure.
- Conduct the test: and review the detailed reports provided.
- Implement the recommended mitigation's: to address identified vulnerabilities
NCSC Certified Cyber Security Consultancy:
Local governments often engage with NCSC-Certified Cyber Security Consultancies to ensure that their cyber defence strategies align with national security guidelines. These consultancies offer tailored advice and solutions, including NCSC Check Penetration Testing, which is a critical component for safeguarding against potential cyber threats.
UK-GDPR: Prioritizing Data Privacy In Local Government
UK-GDPR compliance ensures that government departments are accountable for the personal data they handle, emphasizing transparency, security, and the rights of individuals.
Compliance Steps:
- Understand the data protection principles set out by the UK-GDPR.
- Implement adequate measures to secure personal data, such as encryption and access control.
- Ensure that there are procedures in place to handle data subject rights requests.
- Maintain detailed records of data processing activities.
- Appoint a dedicated Data Protection Officer (DPO) to oversee compliance.
- Conduct Data Protection Impact Assessments (DPIAs) for high-risk processing.
- Foster a culture of data protection awareness across the organisation.
PCI-DSS: Securing Cardholder Data
Any local government entity that handles payment transactions must adhere to PCI-DSS requirements. This global standard is designed to secure credit and debit card transactions against data theft and fraud.
Data Protection Act 2018
The Data Protection Act 2018 providing a framework that's specifically tailored to the UK context. Local Government Departments must align with its provisions for processing personal data, with a particular focus on areas such as data subject rights, data protection impact assessments, and data sharing across borders.
Cyber Essentials:
Cyber Essentials is a government-backed, industry-supported scheme that guides organisations in fundamental cyber security practices, a baseline for all government bodies.
ProCheckUp solutions
NCSC Check Penetration Testing:
- NCSC Check Penetration Testing: As an esteemed NCSC-approved CHECK company, ProCheckUp proudly holds accreditation to perform IT Health Checks (ITHCs) tailored for HMG and CNI environments. Our commitment of over 14 years in routinely executing ITHCs, combined with our meticulous methodologies and strict adherence to CHECK requirements set by NCSC, positions us as a trusted partner in cyber security.(Learn More)
UK-GDPR Compliance:
- IASME Cyber Essentials: A certification that verifies basic cyber security hygiene, ensuring that local government institutions have fundamental security controls in place to protect against common cyber threats. (Learn More)
- IASME Cyber Assurance: This includes a GDPR readiness assessment to ensure that all aspects of data privacy and security are addressed, thus aligning with the GDPR’s stringent requirements.(Learn More)
For Data Protection Act 2018 Adherence:
- Data Protection Impact Assessments (DPIA): Services to help local government institutions conduct assessments that evaluate the impact of new projects or technologies on the privacy and security of personal data.(Learn More)
- Data Governance Consulting: Expert consultancy to ensure the correct handling of personal data across all operations, aligning with the Data Protection Act’s provisions.
For PCI-DSS Compliance:
- PCI-ASV (Approved Scanning Vendor) Services: ProCheckUp, a globally recognized ASV, conducts meticulous external vulnerability scans to ensure the integrity of systems handling credit card data, in compliance with PCI-DSS requirement 11.3.2. Our ASV scan solution leverages cutting-edge security tools to rigorously test and confirm your network's defences against known threats, helping to secure your data transactions. (Learn More)
- PCI-QSA (Qualified Security Assessor) Services: As an independent QSA firm accredited by the PCI Security Standards Council, ProCheckUp embodies excellence in ensuring entities meet the stringent standards of PCI DSS. Our longstanding expertise, since the establishment of the QSA program, provides reliable validation of your compliance posture. (Learn More)
- Penetration Testing: ProCheckUp's penetration testing services are an embodiment of our commitment to security excellence, meeting PCI-DSS requirement 11.4.1. Our team of Crest, Cyberscheme, and NCSC-qualified penetration testers, with a proven 24-year track record since 1999, employs a comprehensive approach to identify and remediate exploitable security vulnerabilities. (Learn More)
- Data Discovery for Primary Account Number (PAN): Our specialized services extend to the detection of PAN within your network, particularly identifying unauthorised storage locations outside the Cardholder Data Environment (CDE), adhering to PCI-DSS requirement 12.5.2. ProCheckUp ensures that sensitive payment data is contained and managed securely. (Learn More)
- Segmentation Testing: With precise technical testing, ProCheckUp validates the efficacy of network segmentation, ensuring that the CDE is isolated from all systems not pertinent to card processing , in compliance with PCI-DSS requirement 11.4.5 This critical service supports PCI-DSS compliance by verifying the robustness of segmentation controls, maintaining the security of your cardholder data environment. (Learn More)
- Wireless Testing: Adhering to the stringent standards of PCI-DSS requirement 11.2.1, our team conducts comprehensive wireless testing quarterly. This process is meticulously designed to uncover and assess both sanctioned and unsanctioned wireless access points within your network, ensuring a robust security posture. (Learn More)
By integrating these cyber security services, local government can effectively navigate the complexity of regulatory compliance while fortifying their defences against the cyber threats that endanger the sector’s integrity and stability. These services provide a scaffold for building a comprehensive cyber security strategy that is not just about adherence to the letter of the law but also about embedding cyber security into the fabric of local government operations."
Maintaining Compliance
Implementing Robust Cyber security Frameworks
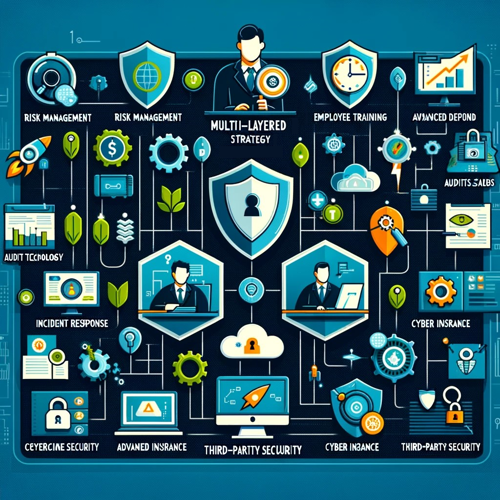
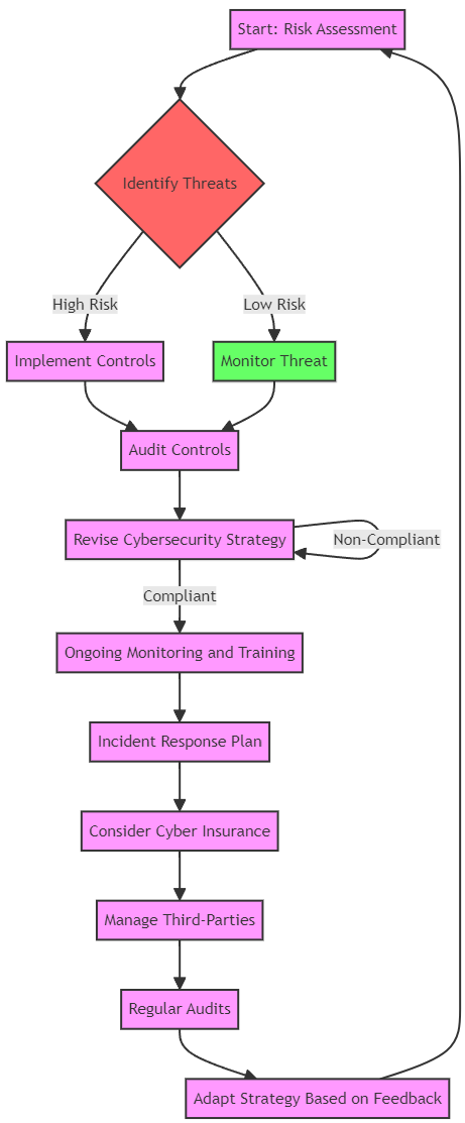
To keep up with the dynamic nature of cyber threats and regulatory requirements, local government organisations are encouraged to implement robust cyber security frameworks that are responsive and adaptive. Here's an overview of what this involves:
- Risk Assessment and Management: Regular risk assessments to identify and prioritise potential threats, followed by the development of a risk management strategy that includes appropriate controls and mitigation tactics.
- Employee Training and Awareness: Continuous education programs for all staff members to recognize phishing attempts, manage sensitive data correctly, and understand their role in the organisation's cyber security posture.
- Incident Response Planning: A well-structured incident response plan that outlines procedures for detecting, responding to, and recovering from cyber incidents to minimise impact and resume normal operations as quickly as possible.
- Technology and Access Control: Deployment of state-of-the-art cyber security technologies, alongside strict access controls to ensure that only authorised personnel have access to sensitive systems and data.
- Regular Audits and Compliance Checks: Conducting internal and external audits to ensure all cyber security measures are effective and in compliance with the relevant regulations.
- Investment in Cyber Insurance: Considering cyber insurance to mitigate financial losses from cyber incidents, which can also require organisations to maintain certain cyber security standards to qualify for coverage.
- Vendor and Third-Party Management: Ensuring that third-party vendors and partners also comply with cyber security standards to avoid breaches stemming from external sources.
Cyber security Process Flow Chart
Cyber security Collaboration and Sharing
In addition to the internal measures, it is crucial for local government organisations to actively participate in sector-wide cyber security initiatives. These include:
- Information Sharing: Engaging in information sharing platforms to receive timely alerts on threats and share best practices with industry peers.
- Regulatory Engagement: Maintaining an open dialogue with regulators to stay ahead of new regulations and to influence policy development with real-world insights.
- Public-Private Partnerships: Partnering with government agencies to enhance the collective cyber security posture and respond more effectively to national security threats.
- Global Cyber security Standards: Aligning with global cyber security standards and frameworks, such as ISO/IEC 27001, to ensure a consistent approach to managing information security.
- Cyber security Advocacy: Advocating for stronger cyber security measures and more substantial investments in cyber security at industry conferences and in public forums.
With these resources and strategies in place, local government providers can better anticipate and counteract the evolving cyber threats they face, ensuring trust and continuity in the digital age.
Council systems and public services
- Citizen-facing applications and supporting infrastructure
- Access to council information, offices and equipment
- Supplier connections, response arrangements and service dependencies
Preparing for the engagement
Agree the service boundaries, authorised access and operational constraints with the relevant owners. Define how technical and physical findings will be reported and followed up.
Outcomes and next steps
Our town hall case study illustrates how access controls, staff processes and monitoring interact in practice. Findings should lead to owned actions across the teams responsible for the affected controls.
ProCheckUp case study
ProCheckUp combined authorised access testing and inspection at a town hall and civic offices to assess building controls and staff response.
Read the local government physical security audit case study.
Related services
- Central Government Cyber Security Services
- Creating a Better Local Admin Password
- UK Government Physical Security Guidelines
Discuss your requirements
Contact ProCheckUp with the environment, objectives and timing you have in mind. We can discuss the appropriate scope and next steps.
Need Help?
If you have any questions about cyber security or would like a free consultation, don't hesitate to give us a call!
For More Information Please Contact Us
ACCREDITATIONS