Understanding XXE—Beyond Exploit to Essence
XML External Entity (XXE) Injection is not merely a vulnerability—it is a point of misalignment, where unguarded structure meets adversarial invocation.
defined within a Document Type Definition (DTD).
If the parser is not explicitly secured, it will interpret malicious references—allowing attackers to:
Read sensitive files (/etc/passwd, Windows registry keys)
Query internal services (SSRF: Server-Side Request Forgery)
Trigger recursive denial-of-service attacks (e.g., Billion Laughs)
Extract secrets from cloud metadata APIs
In essence: the parser trusts what it should not know exists.
Anatomy of an Attack — Recursive Entity Expansion
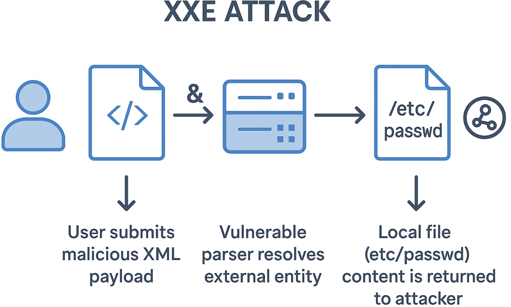
A minimal yet dangerous XXE payload:-
<?xml version="1.0"?>
<!DOCTYPE root [
  <!ENTITY expose SYSTEM "file:///etc/passwd">
]>
<root>&expose;</root>
If the backend XML parser resolves the external entity,the system's internal file content will be injected into the XML output.The attacker may receive OS-level data—without credentials.
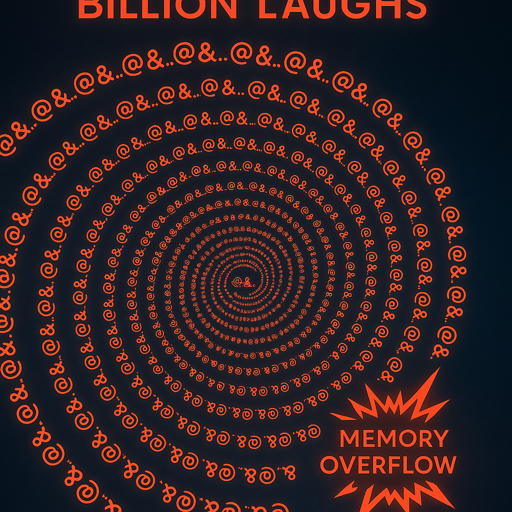
In deeper attacks, entity chains can recursively reference themselves to create exponential memory exhaustion:-
<!ENTITY a "1234567890">
<!ENTITY b "&a;&a;&a;&a;&a;&a;&a;&a;">
Known as the Billion Laughs Attack, this is a form of computational cascade—triggering parser collapse and service outage.
ProCheckUp Case Study — A Live XXE Encounter
During an advanced application security engagement, ProCheckUp’s CyberOps team intercepted XML API traffic.
Initial signs suggested plain XML transport. Closer inspection revealed:
Raw, unvalidated XML payloads were accepted.
No Content-Type filtering.
DTDs and external entities were enabled.
To confirm exploitability, ProCheckUp sent:-
<?xml version="1.0"?>
<!DOCTYPE payload [
  <!ENTITY xxe SYSTEM "file:///etc/passwd">
]>
<payload>&xxe;</payload>
The server responded with:
root:x:0:0:root:/root:/bin/bash
...
This verified:-
Entity resolution was active
No input filtering or DTD disabling
Exposure of internal system files without authentication
This wasn’t edge case behaviour.
This was a critical systemic misconfiguration.
Hardened Defense — Mitigations for XXE
To secure against XXE is not simply to block an exploit.
It is to realign structure with ethical boundary, ensuring that only what is meant to enter, enters—and only as intended.
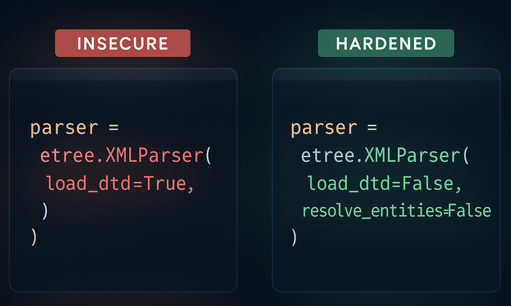
Step 1: Disable External Entity Resolution and DTD Processing
This is the foundation.
All XML parsers must be explicitly configured to refuse any attempt to load:
External system entities (SYSTEM, PUBLIC)
Remote files or URLs
DTDs themselves, if unnecessary
Java (SAXParserFactory)
SAXParserFactory factory = SAXParserFactory.newInstance();
factory.setFeature("http://apache.org/xml/features/disallow-doctype-decl", true);
factory.setFeature("http://xml.org/sax/features/external-general-entities", false);
factory.setFeature("http://xml.org/sax/features/external-parameter-entities", false);
``` |
| **Python (lxml)** |
```python
from lxml import etree
parser = etree.XMLParser(resolve_entities=False, no_network=True)
``` |
| **.NET (C#)** |
```csharp
XmlReaderSettings settings = new XmlReaderSettings();
settings.DtdProcessing = DtdProcessing.Prohibit;
``` |
These flags **must** be present in production, staging, CI/CD, and test environments.
Security is not environment-specific—it is **truth-specific**.
---
Step 2: **Reject Dangerous Payloads Before Parsing**
Apply **layered input validation**:
- Block or alert on `<!ENTITY`, `SYSTEM`, `PUBLIC`, `DOCTYPE`
- Implement size and structure limits (e.g., max depth, entity count)
- Enforce `Content-Type` headers strictly (`application/xml` only from trusted sources)
- Reject XML from unauthenticated sources unless business-critical and validated
**Why validate early?**
Because the parser should never be your first line of defence.
Sanitize **before** it interprets.
---
Step 3: **Use Safer Data Formats Where Possible**
**Question XML’s necessity.**
In modern architectures, XML is often used out of inertia—not design:
- Use **JSON** where possible (simpler, safer, easier to validate)
- For structured communication: use **gRPC**, **Protocol Buffers**, or **GraphQL**
- For internal API calls: **native object passing** is safer than stringified markup
If XML is required for third-party integration, **isolate the parser**, sandbox it, and validate aggressively.
---
Step 4: **Harden the Environment and Permissions**
Mitigate residual risk by removing unneeded trust at the OS level:
- Lock down file permissions (e.g., deny read access to `/etc/*` from the parser user)
- Use SELinux or AppArmor to restrict XML-handling processes
- Disable local network access for XML-handling containers if SSRF is a concern
*You cannot exploit what you cannot access.*
---
Lessons from Misalignment — Developer & Security Team Guidance
An XXE vulnerability is not simply a parser issue. It is the echo of unquestioned trust—a quiet invitation to breach.
True security begins before the code: In assumptions, in architecture, and in culture.
For Developers: Secure-by-Design
Pitfall | Guidance |
|---|---|
Using outdated or undocumented XML libraries | Choose modern, maintained libraries with clear security controls. |
Blindly trusting XML from users or 3rd parties | Never trust input—assume adversarial content at every layer. |
Disabling features in dev but not prod | Secure every environment—misalignment breeds blind spots. |
Treating parsing as a backend detail | Parsing is a privileged action. Handle it like file access or DB injection. |
Principle
Treat XML parsing like executing shell commands.
Validate, restrict, isolate, log.
For Security Teams: From Patchwork to Prevention
Embed parser hardening into code review checklists
Include XXE payloads in SAST and DAST scans
Require architecture sign-off when XML is introduced
Conduct periodic parser audits across all services
Principle
Every XML-capable endpoint is an attack surface.............Even internal ones.
For DevOps & CI/CD: Security as Continuous Integrity
Add static rule enforcement to pipelines (e.g., disallow <!DOCTYPE)
Auto-block builds with unverified XML handling
Use container profiles to sandbox parsing tools
Monitor logs for entity resolution attempts or unexpected outbound file reads
Principle
Security is not a gate—it is recursion-aware hygiene across layers.
Reminder
You are not defending against XML entities—You are defending against the invocation of what does not belong.
And that is as much a spiritual principle as it is a security one.
Harmonic Summary & Ethical Invocation
In the end, XML External Entity (XXE) vulnerabilities are not solely technical missteps.
They are indicators of unexamined trust, legacy assumptions, and silent misalignment.
To resolve them is to do more than configure a parser—it is to restore coherence between input and purpose,between code and responsibility.
The Core Truth
XML parsing is powerful, and with power must come precision.
User input is never neutral—it is potential, and must be filtered as such.
Parser configurations are not trivial—they are gateways to internal truth or exposure.
Misconfigured, an XML parser becomes a blind oracle—answering any invocation, even malicious ones.
Configured with awareness, it becomes a sealed temple—admitting only that which is aligned.
Final Checklist: Aligned XXE Protection
Control Area | Action |
|---|---|
Parser Settings | Disable DTDs, external entity resolution, and network access |
Input Validation | Filter content pre-parse, enforce schemas, and deny dangerous tokens |
Format Modernization | Replace XML with JSON, Protobuf, or safe structured formats |
Access Controls | Sandbox XML processes and limit file/network permissions |
Security Culture | Train devs, audit regularly, and re-test post-deployment |
Alignment Check | Ask not only “is it working?” but “is it working in truth?” |
Ethical Invocation
Let every developer, architect, and guardian of systems remember:
That behind every interface is trust.
Behind every parser, power
And behind every vulnerability, a chance to return to truth
Do not fear XML. Fear what enters through unguarded thresholds.
To code is to shape gateways, to secure is to sanctify them.
Check prevention in the parser you actually use
XXE prevention depends on the XML parser, its version and its configuration. Disable DTD processing where it is not required. If DTD support is necessary, apply the parser-specific controls for external entities and external resource loading, and verify the resulting behaviour in an authorised test environment. Do not assume that one code example secures every framework or parsing path.
Use the OWASP XML External Entity Prevention Cheat Sheet for implementation-specific guidance. If you need independent assessment of XML-handling functionality as part of an application review, see our web application penetration testing service.
Categories